Workload Pricing: More Value from Splunk Cloud
.conf & .conf Go Splunk
And it’s exactly what brought me to Splunk earlier this year: our differentiated approach has enabled organizations to turn data into doing to deliver secure and resilient systems to unlock innovation. When a transformative cloud strategy is built on a strong data foundation enabled by Splunk, the sky’s the limit. Which is why Splunk continues to evolve our capabilities and user experience to make it easier (and faster!) to get value from Splunk.
We listened and we heard you. You asked for the flexibility to run workloads when you wanted, and on the data you wanted. That’s why we introduced one of our biggest changes in recent years, and one that we are now making available to all Splunk Cloud customers. At .conf21 today, we were thrilled to announce Workload Pricing for All. I’d like to offer context about how this pricing approach accelerates the power of Splunk Cloud.
We first debuted workload pricing a few years ago to give customers the flexibility and choice to work smarter across more use cases. With this structure, you're NOT metered on data you ingest into the Splunk platform, but instead on when you engage in tasks. This ensures that users have the freedom to put more data into the Splunk platform, and the choice to use it when they want to bring even more value to their organization. That’s the speed and scale; when it comes to efficiency, the typical Splunk customer enjoys nearly triple the time available for high-value use cases when they move to Splunk Cloud.
While we can celebrate the value of these new pricing models, our customers and partners are our source of truth. I’m excited to share one of many great customer outcomes this new model has enabled.
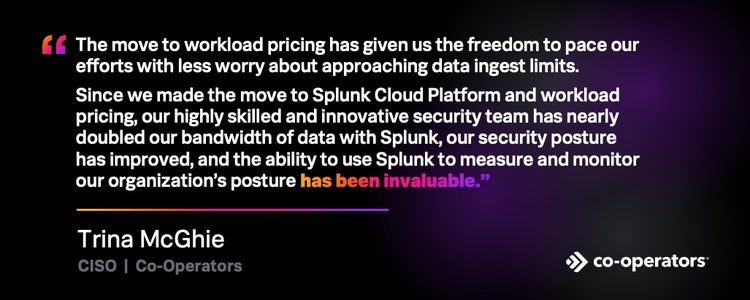
One of Canada's leading insurers, Co-operators, has achieved great success with Splunk Cloud, Splunk SOAR, and workload pricing. This combination has helped CISO Trina McGhie take action on more data, quickly arming her highly skilled security team with the insights they need to vastly improve the company's security posture:
I am really excited at how we’ve enabled more users to get more value from their investment in the Splunk platform. The sheer scale, reach, and speed of our platform is unmatched, and now that workload pricing is available to all Splunk Cloud customers, so is the value it unleashes.
This is all about freedom and flexibility for you. YOU decide how to leverage Splunk, and where and when to get the most value.
Read more:
- 99 Data Problems and Pricing Ain’t One
- Splunk Workload Pricing For the Win!
- Workload Pricing and SVCs: What You Can See and Control
- What is Splunk Virtual Compute (SVC)?
Follow all the conversations coming out of #splunkconf21!
----------------------------------------------------
Thanks!
Teresa Carlson
Related Articles
Eliminate Manual Threat Analysis of Credential Phishing & Malware Threats with Splunk Attack Analyzer
!pip install DEV from .conf24