Next Level Automation: What’s New with Splunk Phantom
Security Splunk
If we can support two playbook runners, then why not more!?
With the release of Splunk Phantom 4.10.1, that’s exactly what we did. We now allow you to configure the number of playbook runners, using Python 2 and Python 3. (We call it “vertical scaling.”) It helps you to scale automation at your organization. By configuring multiple playbook runners, a single Splunk Phantom instance can now handle, run and execute multiple actions from different playbooks simultaneously.
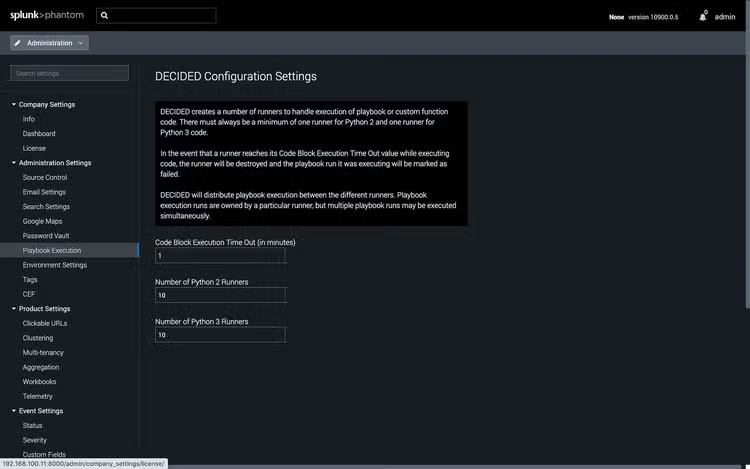
Previously, Splunk Phantom was able to kick off one action at a time, creating an artificial bottleneck that wasn’t directly related to system resource utilization. The only resolution for environments experiencing this bottleneck was to move to a cluster model (or add new nodes if they were already in a cluster). In a 4.10.1 world, additional playbook runners can now be used to share the load and ensure Splunk Phantom gets the most out of the resources available to it. Vertical scaling not only allows your playbooks to run concurrently, which saves time; it also enhances performance while reducing the need for managing additional costly hardware.
Ready to try it for yourself? Check out the 4.10.1 release notes or download Phantom 4.10.1 to take advantage of the latest updates.
----------------------------------------------------
Thanks!
Ian Forrest
Related Articles
What Do Organizations Value Most in a SIEM/Security Analytics Provider? In a Word: Actionability
EO, EO, It’s Off to Work We Go! (Protecting Against the Threat of Ransomware with Splunk)
