Monitoring and alerting for activities of expired user accounts
Security Matthias MaierHello,
When it comes to insider threats and user activity monitoring, I see a very common use case that works extremely well across multiple industries. I want to share it with you in this blog post.
Monitoring and alerting for activities of expired user accounts

Your company can have a lot of different user accounts – not just the internal employed worker. There might be more focus on external contractors who move in and out more often or even B2B portals with intellectual property exchange.
If you need to monitor expired accounts, it comes down to the following:
You need to have the username, expire date and user activity data. To get the expire date information is some homework.
Here are two pieces advice:
-
Get the expiry date from the HR department
- This might seem odd. But often the link between HR information and IT information is not completely intact. With your use case you can fix that and make it clear that there are enhancements required. With the Splunk DB Connect App you can easily get this information into Splunk and add it to your identity informations using |inputlookup and |outputlookup. By doing this you find broken synchronization scripts, as well as old but still active user accounts in your environment that need to be cleaned up.
-
Create identities to correlate usernames
- If you’re working in an environment in which a user has multiple user accounts and not just their active directory account you need to maintain identities. An identity is a unique name like the full employee name or the employee number. You then maintain all assigned user accounts to this identity. An example: Tom needs to logon to some systems with his e-mail address (tom@mycompany.com), in some with his sAMAccountName (tom) from Active Directory and to others with his employee number (0815). For some of them his passwords are not connected/synced with Active Directory. So you need to have an identity list/overview to ensure you can map each of those accounts to Tom and his expiry date that you recieived from the HR department.
Once you have done this, you have already enhanced your visibility and security maturity for your company. From there, you can keep on top of unauthorized activities and find any broken business processes.
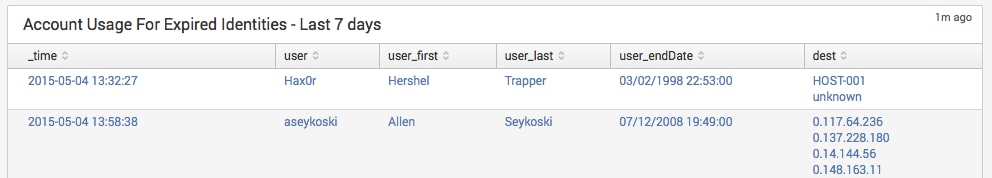
What you’ll discover when an event is generated?
-
-
Applications and scripts that are running in the user’s context
- If it was a technical person that is leaving the company he – by mistake and not following best practice policies – may have run some applications under his user account. When he leaves, those applications are still running and if the account is disabled, they are the first services that crash. So you can be sure that even if the account is disabled 1-2 weeks after he leaves, that application won’t work anymore. Make sure to follow up quickly to fix that with a service user that has the proper permissions.
-
Applications that are not linked to HR Systems / script is not running for user sync
- You will identify that there are applications that have their own user account management and are independent of centralized services. Often those applications are the most critical ones as no one from “outside” (within IT) should be able to get into it. Monitoring and regular reporting about usage should be done on these applications. In large companies this could be things like wire transfer systems that are not automated or the last manual step for a automated business process.
-
Former employees accessing or using company resources
- Often services are available from outside the company, e.g. from the web. Former employees will try to check if their account is still active or not. Make sure you have visibility if they try – and potentially it would make sense to also let the ex employees know that you’re tracking those activities that are unauthorized.
-
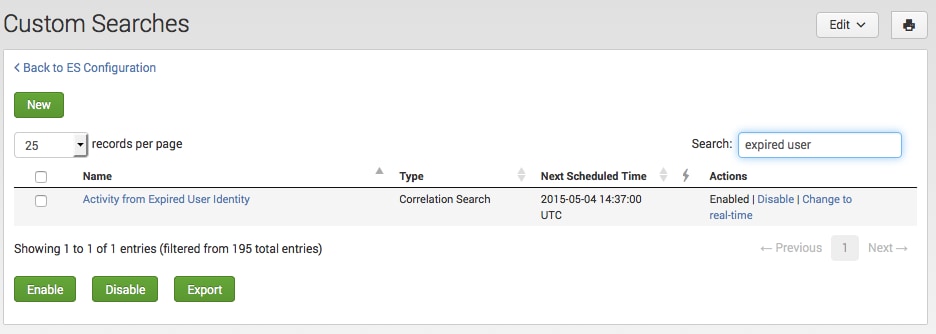
Happy Splunking,
Matthias
Related Articles
Threat Advisory: SwiftSlicer Wiper STRT-TA03
Splunk .conf26: Proving the Agentic SOC in the Center of the Community
