Announcing Splunk Add-on for Microsoft Cloud Services
Platform Elias HaddadI am pleased to announce the availability of Splunk Add-On for Microsoft Cloud Services. Released on April 1st 2016, this add-on which is available on Splunkbase, provides Splunk admins the ability to collect events from various Microsoft Cloud Services APIs. In this first release, this includes:
- Admin, user, system, and policy action events from a variety of Office 365 services such as Sharepoint Online and Exchange Online and other services supported by the Office 365 Management API.
- Audit logs for Azure Active Directory, supported by the Office 365 Management API.
- Current and historical service status, as well as planned maintenance updates for a variety of services supported by the Office 365 Service Communications API.
If you are wondering what use cases could be achieved by ingesting this data into Splunk Enterprise or Splunk Cloud, following is a small sample:
- Track all your Sharepoint Online user and admin level activities. Activities include file and folder actions such as view, create, edit, upload, delete and download; that in addition to file sharing and collaboration.
- Track Azure AD authentications by users, IPs for all of your Microsoft Cloud apps such as Skype, Yammer, Exchange Online and other Office 365 apps.
- Whether it is Skype, Yammer or any other Microsoft cloud service, track the availability and scheduled maintenance windows of these services
- Track Exchange online admin and user activities.
- Track user adoption by browser and geo locations
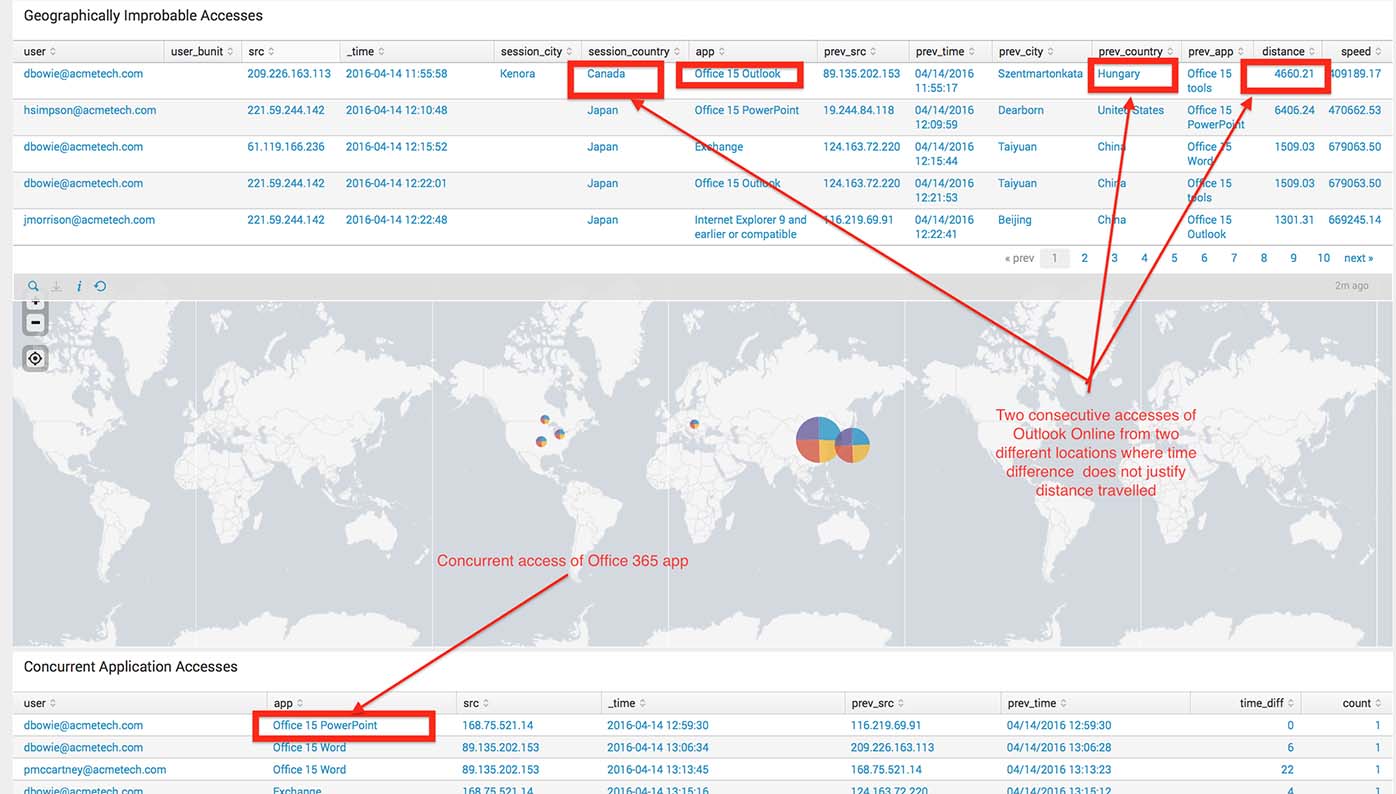
- This add-on is CIM compatible. This means that by using Splunk Enterprise Security, you can address a myriad of security focused use cases such as improbable access detection (snapshot below):
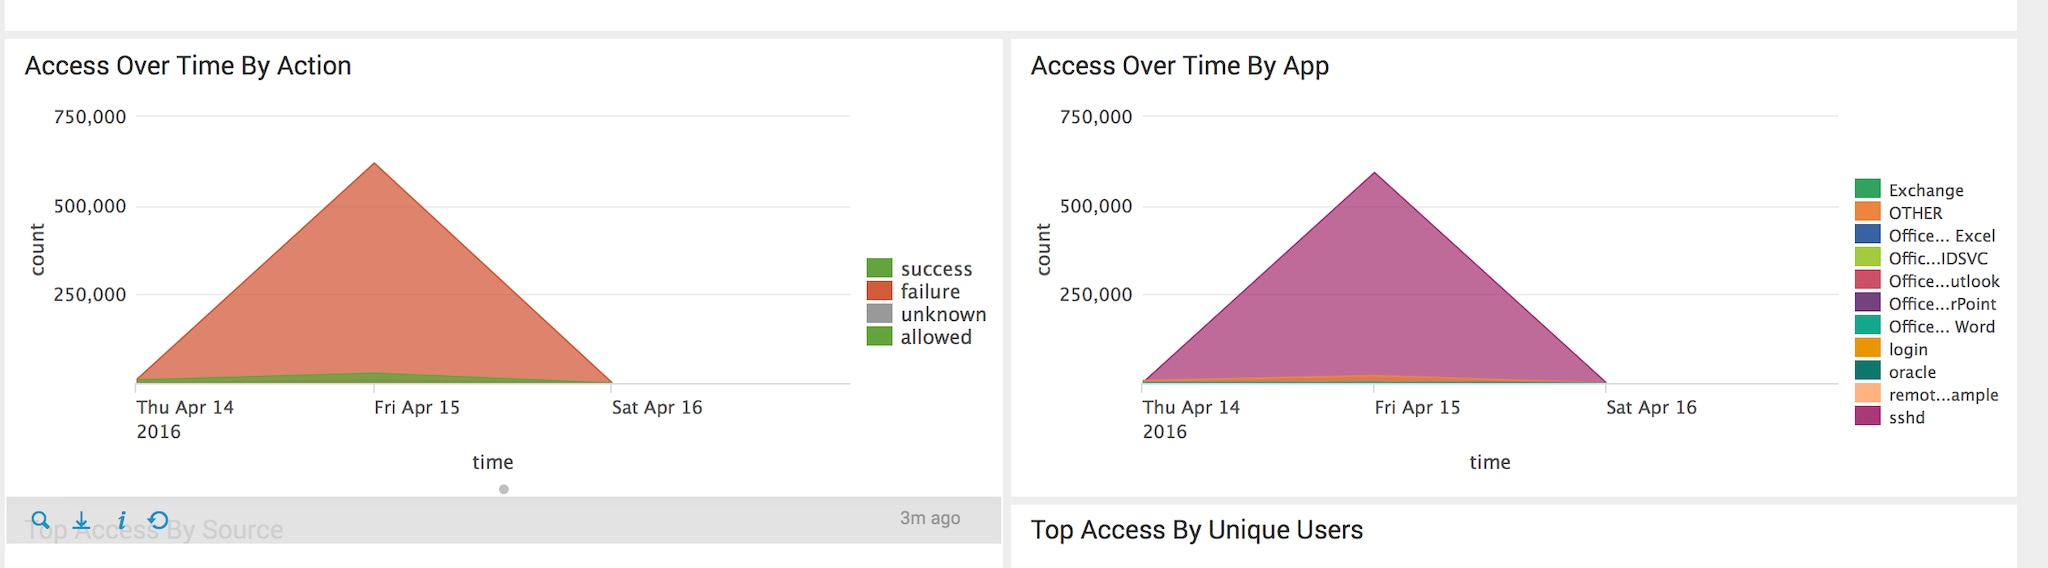
- Office 365 apps access anomaly detection (snapshot below):
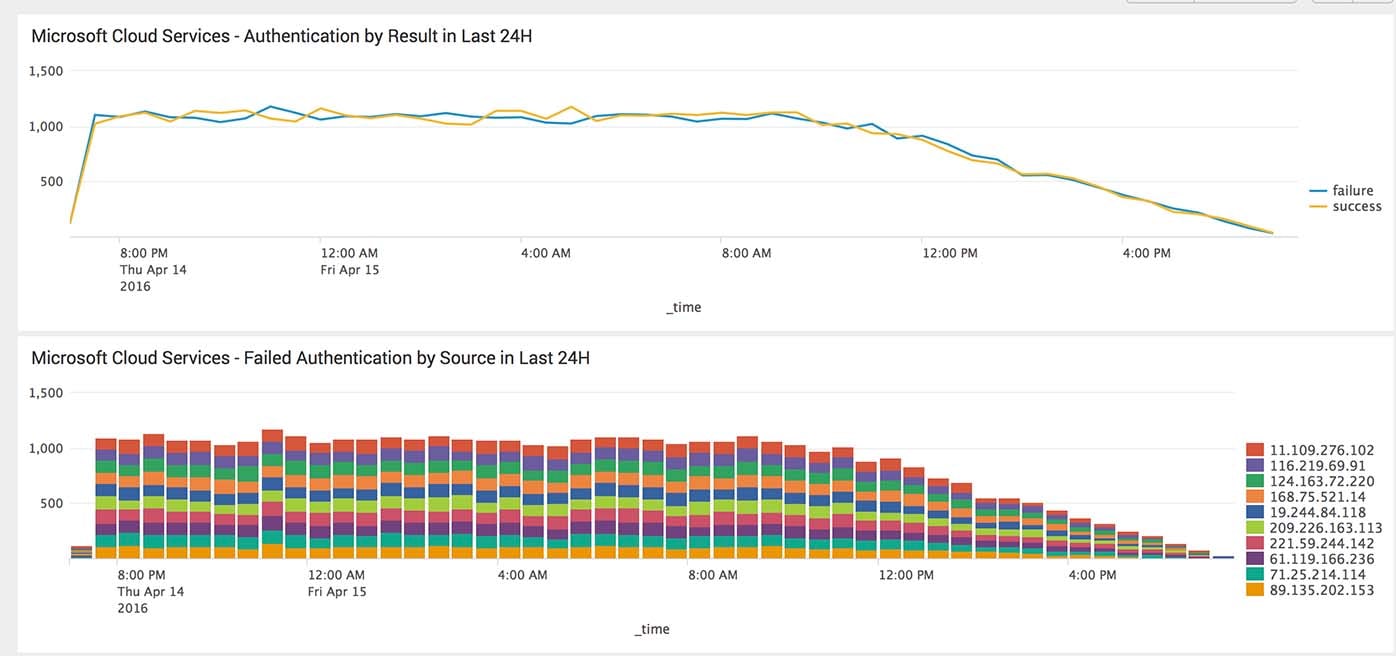
- Using the prebuilt panels that come with the add-on, you can get a quick start to building out your own dashboards. These are some of panels that are included in this release:
Last but not least, the configuration of this add-on supports OAuth v2 allowing you to run the setup without having to save any Azure credentials on your Splunk instance.Please give Splunk Add-on for Microsoft Cloud Services a try and let us know your feedback.
Happy Splunking!
Related Articles
From Vision to Value: New Splunk Platform Innovations Supporting Cisco Data Fabric Are Generally Available
Machine Learning at Splunk in Just a Few Clicks