Splunk Releases Add-On for Google Workspace Security Monitoring
Partners Splunk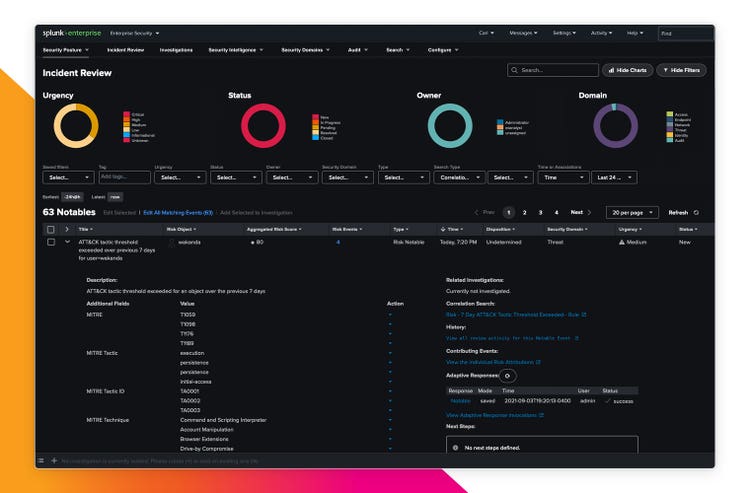
Splunk Add-On for Google Workspace 2.0 includes these exciting updates and additions:
- Gmail: Analyze email metadata to help detect phishing, spoofing, malware distribution, spam, data exfiltration and other email-focused attacks.
- Google Drive: Monitor user activity in Google Drive to detect suspicious activity that could indicate abuse or an attack. Get visibility into items such as unsafe content, sensitive document access, suspicious visibility, and access changes.
- Google Workspace: View login trends for users and key security events such as leaked passwords, failed logins, blocked logins, and suspended users.
- Delegated Authorization: Issue and revoke Oauth tokens.
- User Administration: Create, delete, grant, and revoke privileges.
- Consumption: Analyze and monitor user logins, authorized apps, locked accounts, and other usage metrics.
- Proxy Support: Configure operation behind an HTTP proxy.
- Event Splitting: Create more granular events to make searches and detections faster.
By using the new version of Splunk Add-On for Google Workspace, administrators will be better able to detect and quickly mitigate a wider set of potential attacks from phishing, malware distribution, suspicious user activities and user administration. The extended monitoring provides organizations the ability to offer their users more secure critical productivity and collaboration tools from Google Cloud. Splunk always urges customers to monitor user activity in a way that respects user privacy and follows Google privacy safeguards.
You can learn more about Splunk Add-On for Google Workspace in the user documentation.
Splunk is already working on the next update to the integration, which will focus on delivering even more event types prepared for normalized and performant search use cases. Stay tuned for details of our next installment. We hope to see you at .conf22!
----------------------------------------------------
Thanks!
Mark Karlstrand
Related Articles
Splunk and Mandiant: Formidable Defense Against Attackers
Capitalizing on Cloud to Drive Greater Value from Data and Analytics Insights: A New Accenture Splunk Business Group