Splunk Threat Intelligence Management
Learn Olivia HendersonKey Takeaways
- Splunk Threat Intelligence Management centralizes and streamlines the collection, normalization, and enrichment of threat intelligence from multiple sources, making it actionable and accessible for security teams.
- By automating workflows and integrating with existing security tools, Splunk TIM enables organizations to reduce manual processes, improve detection accuracy, and accelerate threat investigation and response.
- Deep integration with the broader Splunk platform empowers analysts to operationalize threat feeds for hunting, incident response, and reporting, ultimately enhancing overall cybersecurity posture.
Looking for Splunk Intelligence Management? We’ve made some updates — learn more here.
What is Threat Intelligence Management?
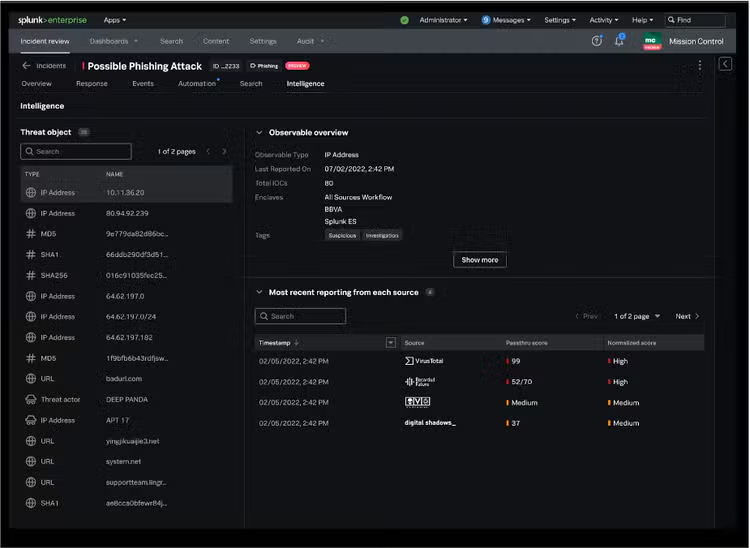
Threat Intelligence Management provides SOC analysts actionable intelligence with associated normalized risk scores and the necessary context from intelligence sources that are required in order to detect, prioritize and investigate security events.
As a feature of both Splunk Enterprise Security (ES) and Splunk Mission Control, Threat Intelligence Management* enables analysts to fully investigate security events or suspicious activity by providing the relevant and normalized intelligence to better understand threat context and accelerate time to triage.
Benefits
With Threat Intelligence Management your team can:
- Gain more context around risk and threats targeting the organization with a full breadth of embedded intelligence from data feeds such as; open-source, technical indicators, malware analysis tools, and threat intelligence reports.
- Reduce noise and surface the highest fidelity intelligence for action through normalized scores from different sources.
- Simplify security workflows by accessing intelligence within Splunk’s leading SIEM and unified workspace, Splunk Mission Control, that provides analysts the right intelligence, at the right time.
(Learn more about Threat Intelligence Management.)
*Initial availability to eligible AWS customers in select US regions only.
Learn more about Splunk Enterprise Security
Interested in learning more about Splunk Enterprise Security? We’ve got you covered! Take a guided tour now or talk to your account manager.
Check out Splunk Enterprise Security
More Splunk resources
- Splunk Lantern: Using threat intelligence in Splunk Enterprise Security
- Docs for Splunk Intelligence Management (Legacy)
And here are more destination for support across the Splunk ecosystem:
- Splunk Docs, where you’ll find all the technical specs for our products.
- Splunk Lantern, where you can self-serve your way to achieving business use cases with Splunk products.
- Splunk Training & Certification, where you can take a variety of courses or follow learning paths towards Splunk expertise.
- Splunk Community, where you can ask questions and get answers from users and experts.
Related Articles
Energy-Efficient Computing: How To Cut Costs and Scale Sustainably in 2026
What Is a Watering Hole Attack? Detection and Prevention