Product Announcement
Exposure Analytics is a capability within Splunk Enterprise Security
Splunk Enterprise Security (ES) delivers a unified SecOps platform, seamlessly integrated with agentic AI, SOAR, UEBA, and SIEM.

Automatically discover entities and accelerate investigations with real-time context.
HOW IT WORKS
Eliminate the blind spots. Automatically maintain a current inventory of entities by leveraging your existing Splunk data. Eliminate outdated, inaccurate, or incomplete entity information and gain real-time visibility across your asset attack surface.
Shift from data gathering to decision-making. Close the identification gap by automatically enriching every alert with historical attribution and entity relationships, linking users to devices over time. By providing context into "who, what, and where" the moment an alert fires, analysts can eliminate the manual research loop and improve MTTR.
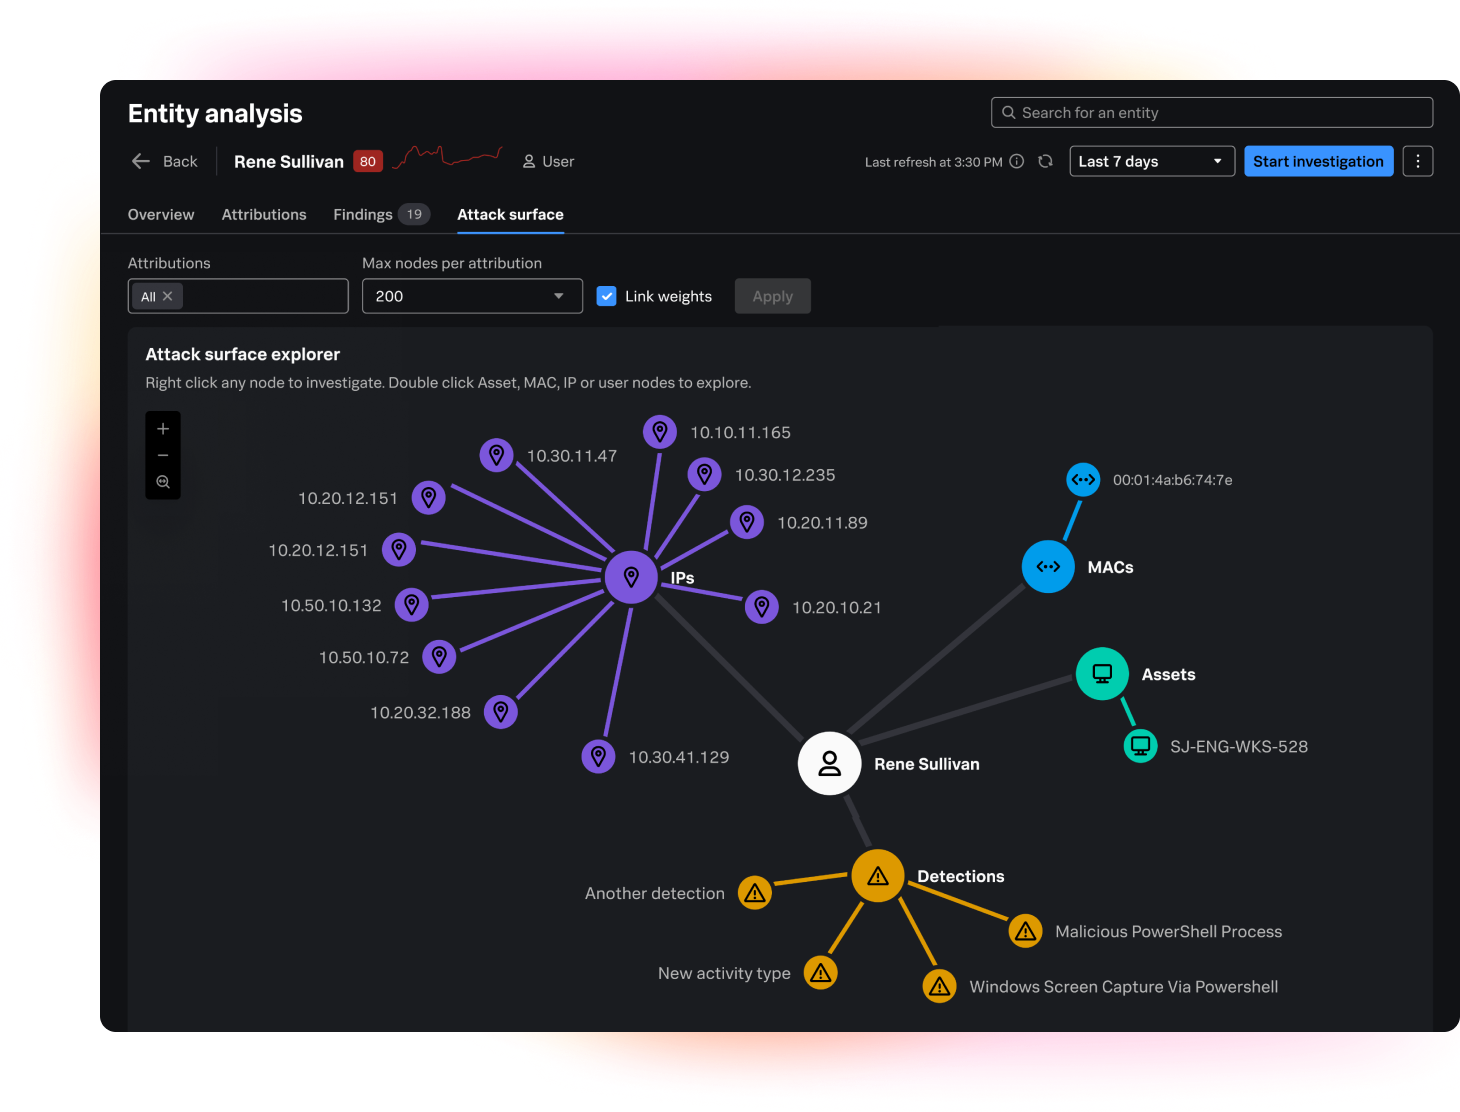
Break the cycle of reactive security by identifying and hardening critical exposures before they escalate into incidents. By unifying dynamic entity risk scoring with deep attack surface visibility, Exposure Analytics empowers your team to pinpoint security gaps and remediate vulnerabilities in real time — ensuring you can proactively close coverage gaps and strengthen your environment’s resilience against the next generation of threats.
Gives analysts the context they need to understand incidents faster and quickly act with confidence.


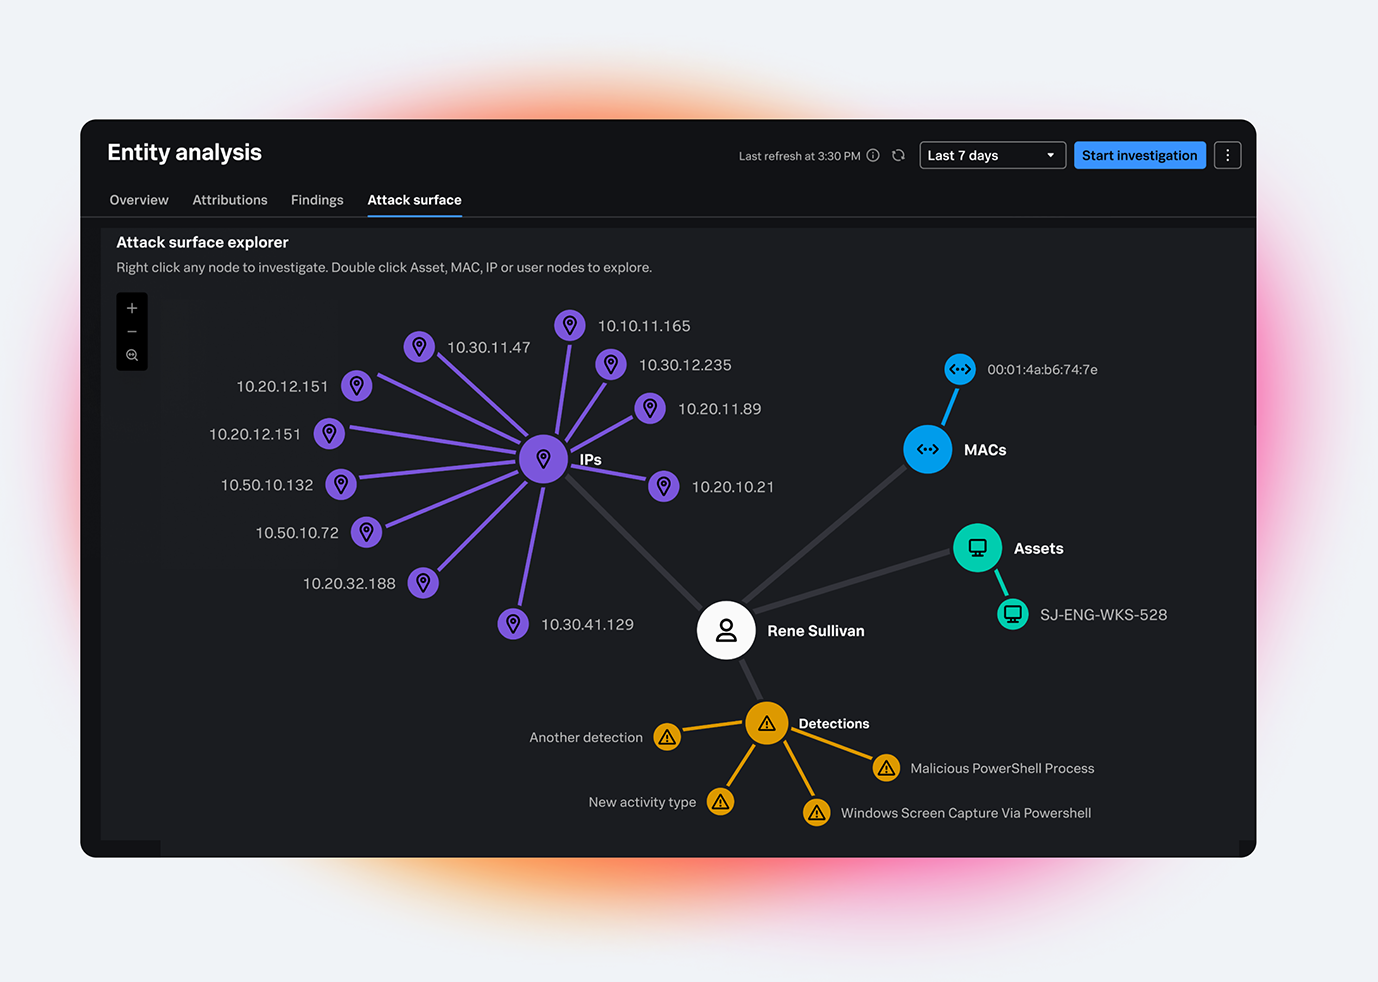
See the full story with entity enrichment and analysis
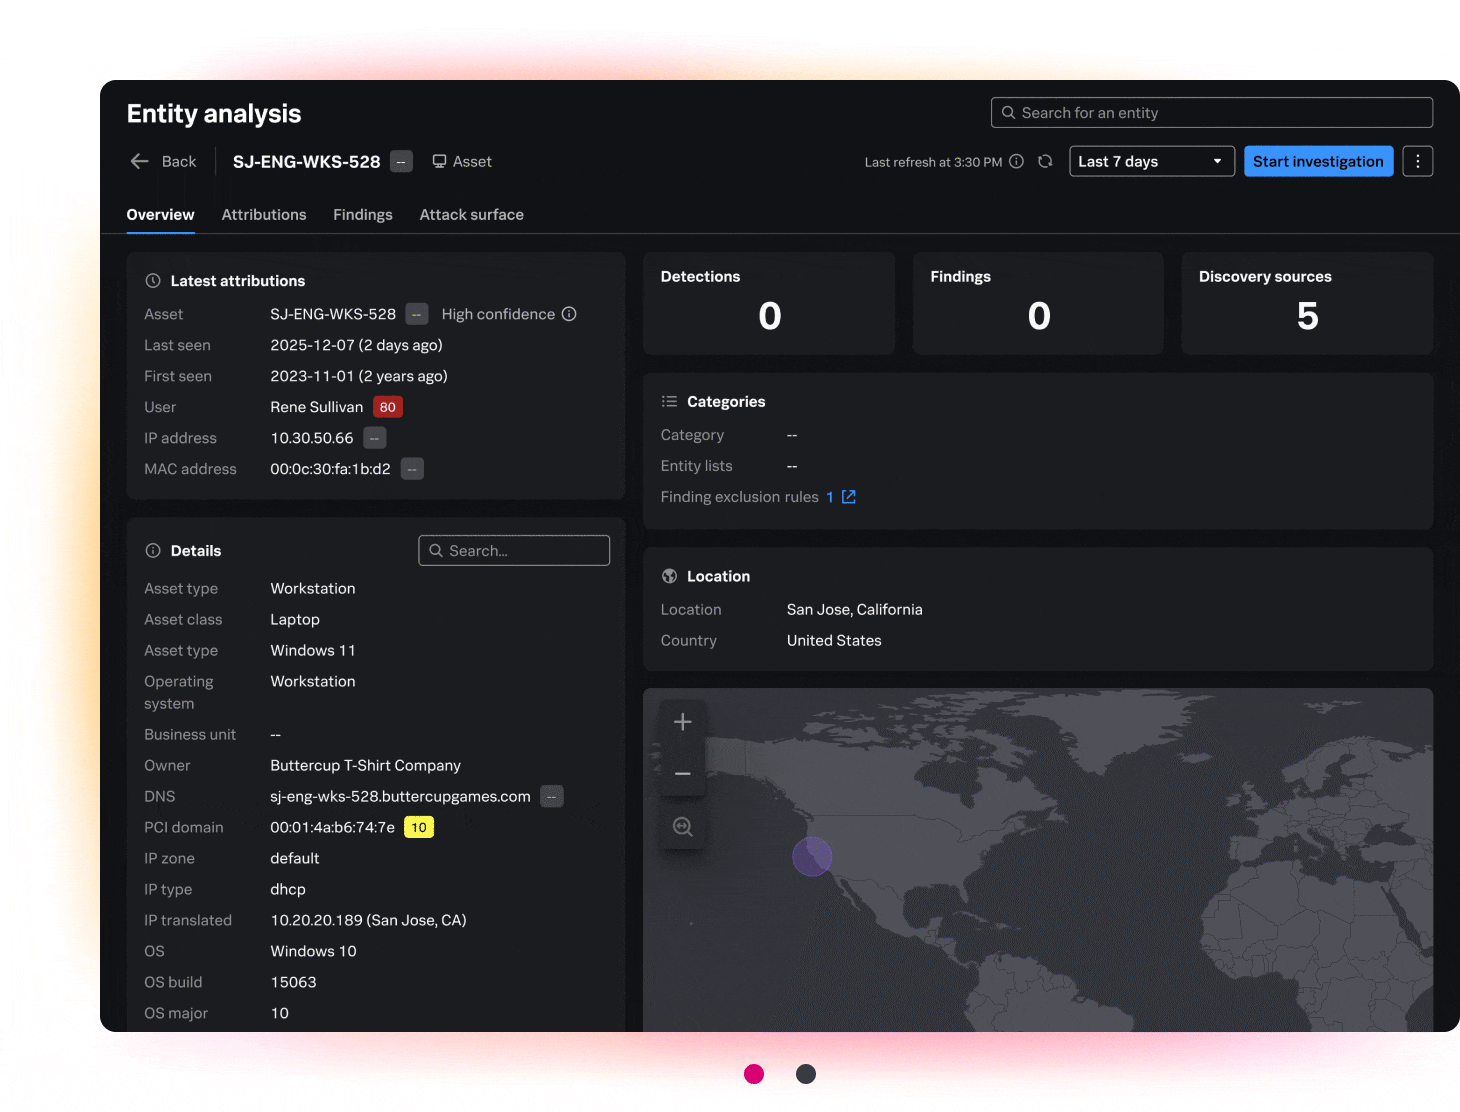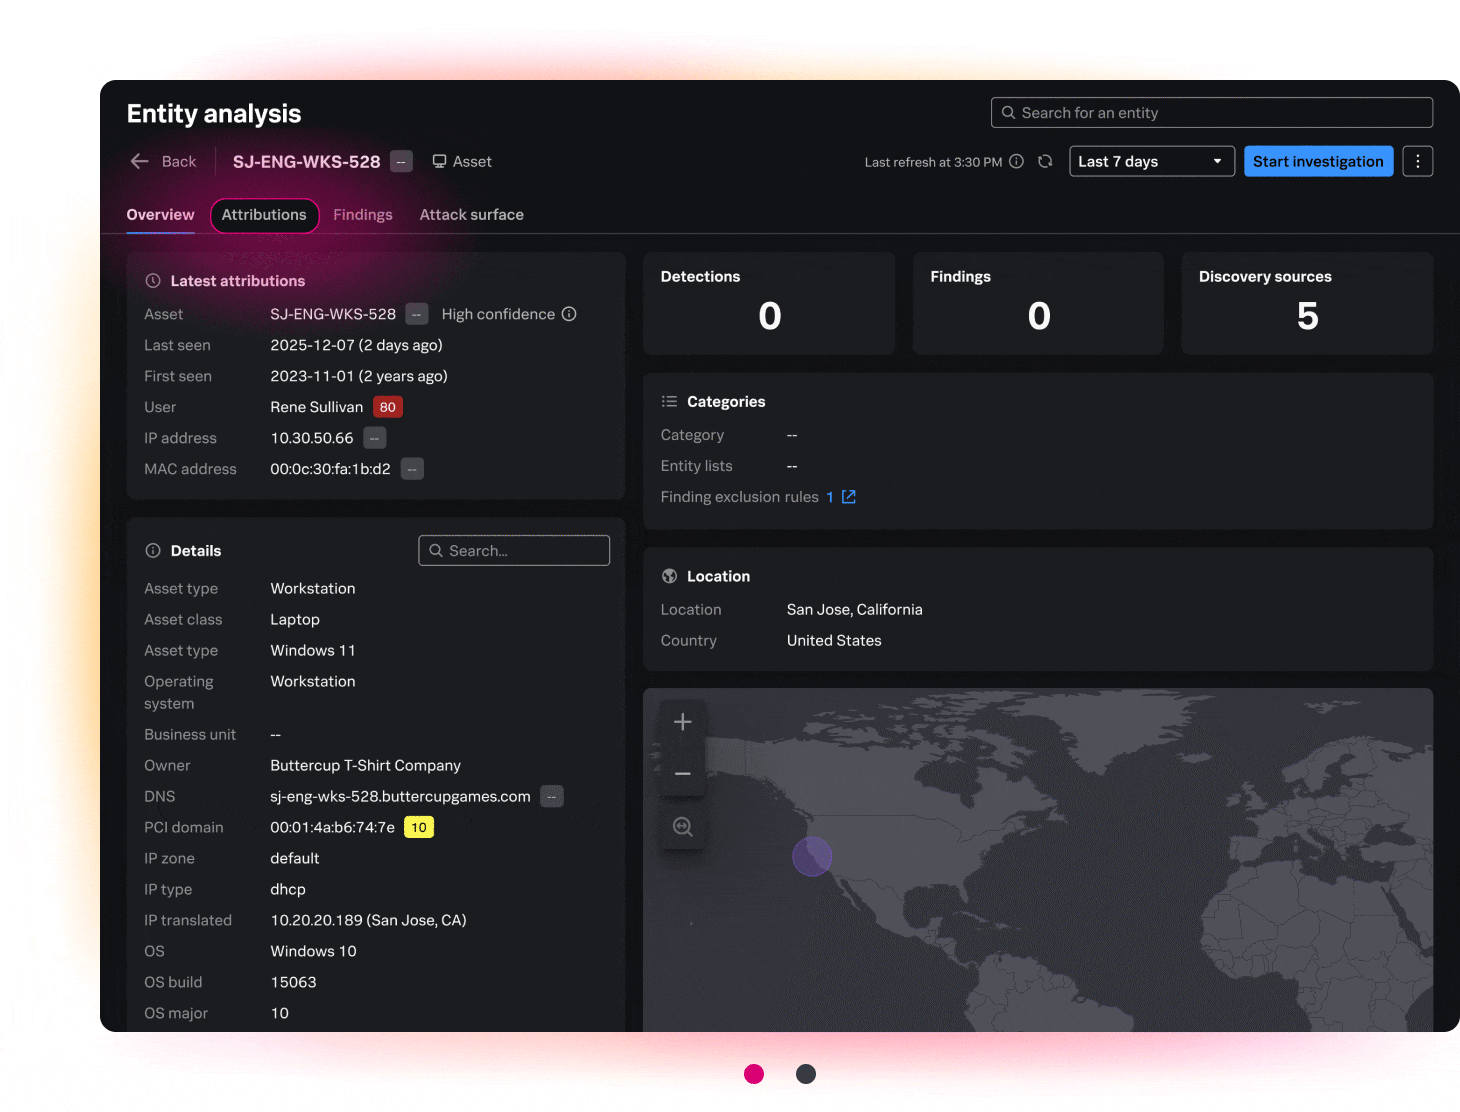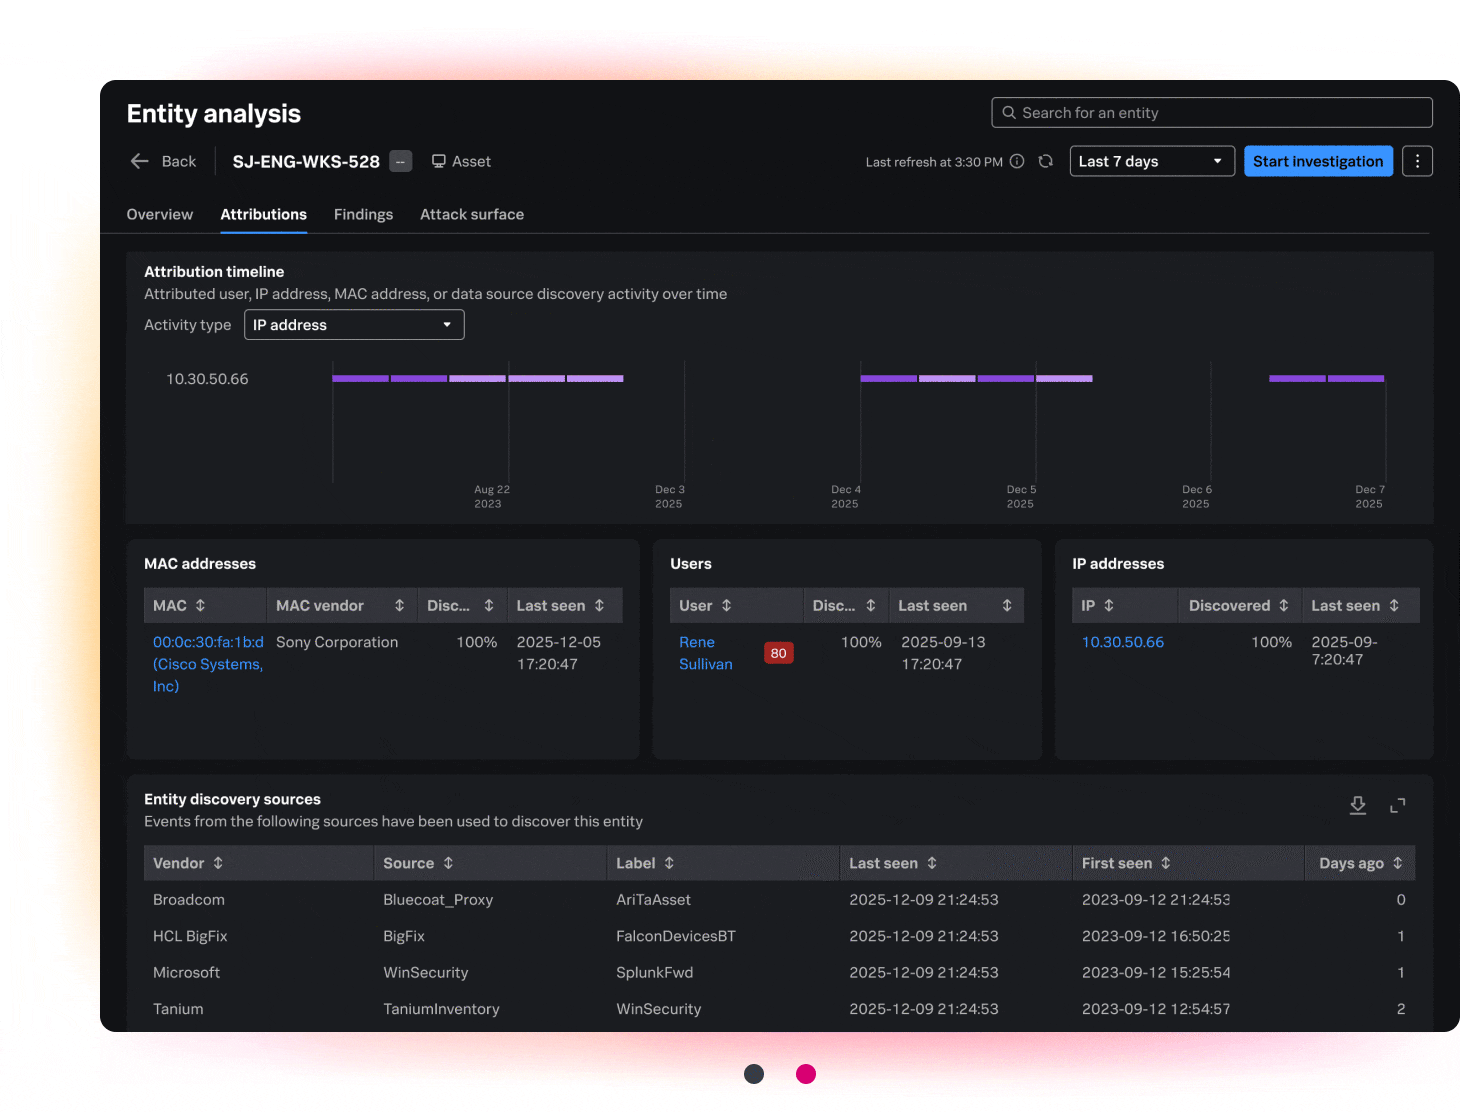
Maintain a continuous, time-stamped record of asset changes and user movements to identify anomalies and understand how an entity’s state has evolved. Link relevant entities and context to detections and findings, while also obtaining the full “who”, “what”, and “when” behind each alert, reducing manual research, accelerating root cause analysis.

Gain immediate, actionable insights across your environment
Proactively identify security control gaps, reduce attack surface, support remediation efforts, and strengthen overall security posture. Visualize exposure trends such as OS distribution, legacy operating systems, and default user account usage, then drill down into inventory and analysis views for deeper investigation.
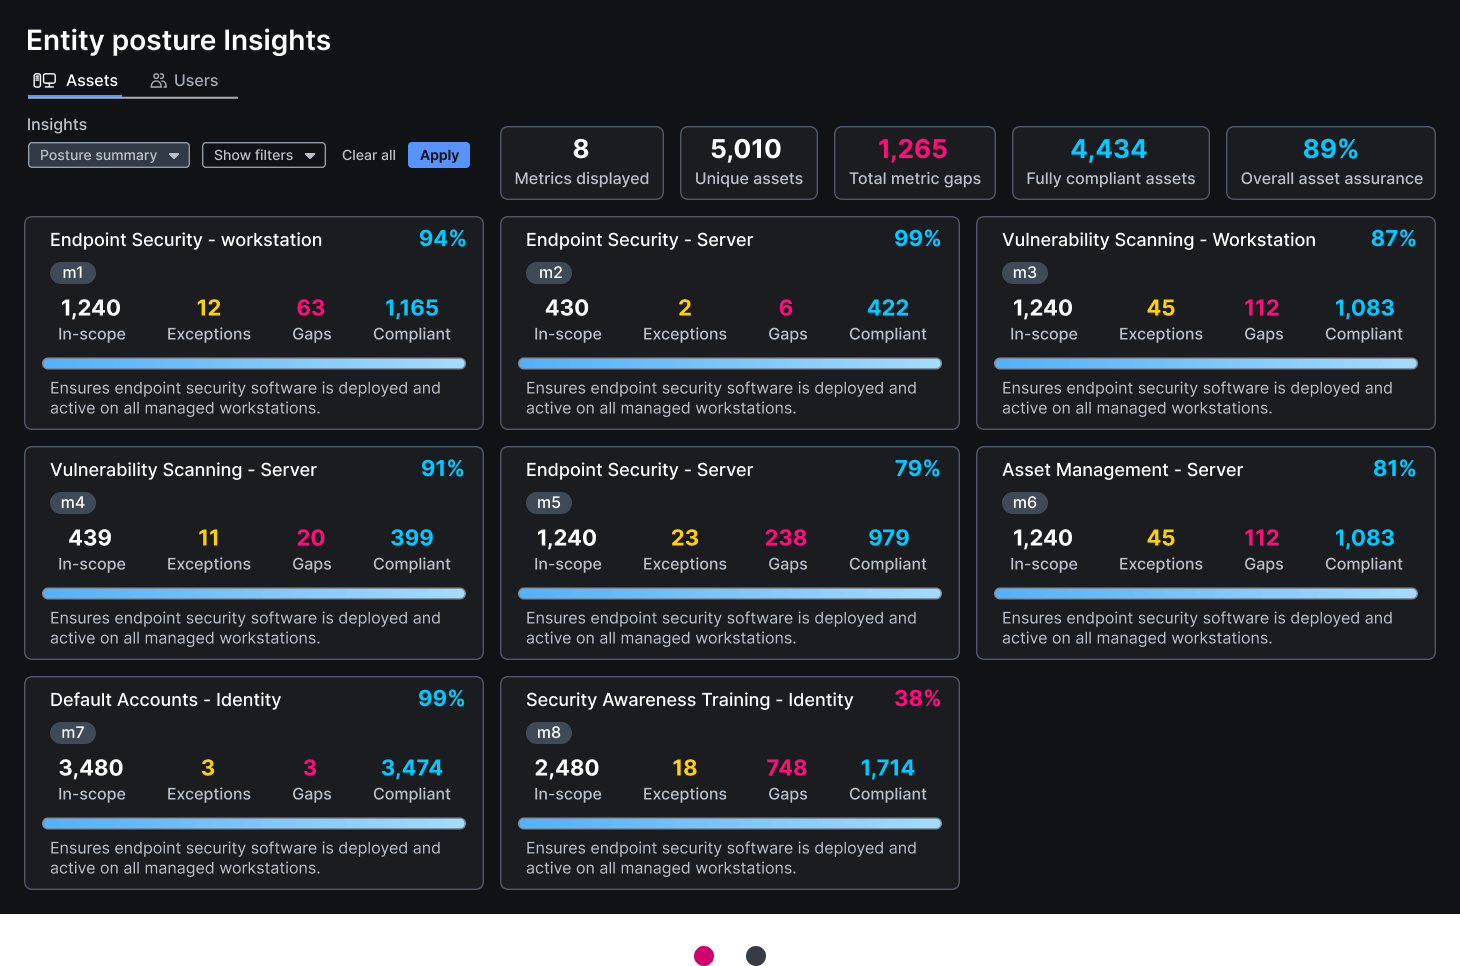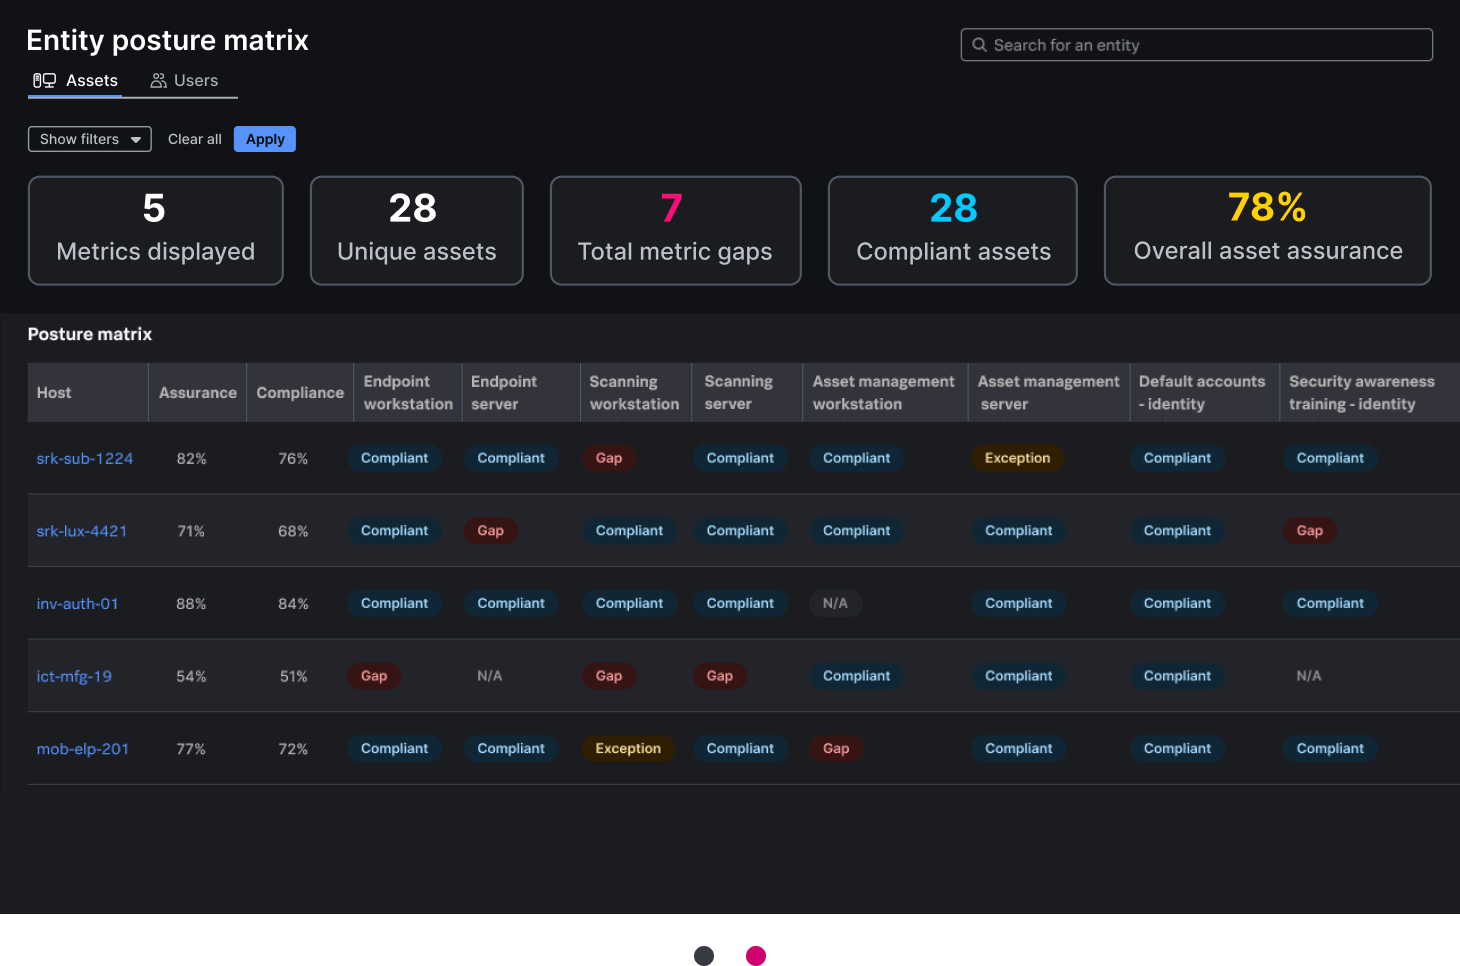
Optimize your security posture with continuous, automated metrics
Monitor continuous and automated metrics into your security posture, helping to prioritize improvements, demonstrate progress, and support regulatory reporting. Track remediation progress, control gaps, and posture improvement over time. (Coming soon)
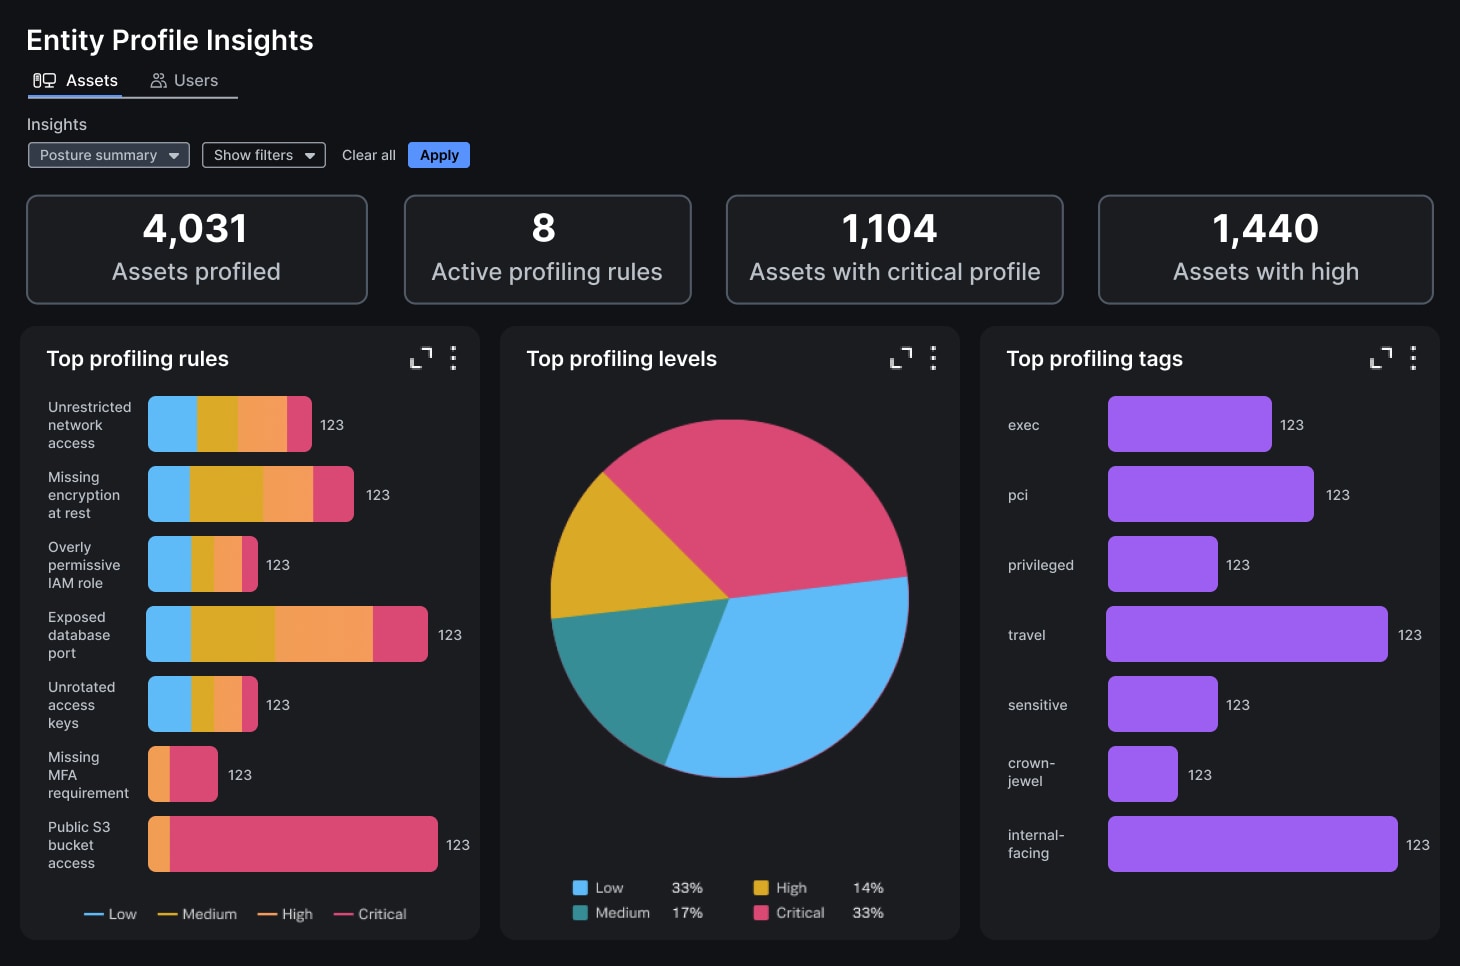
Know which entities matter most — and why
Entity Profiling continuously combines business context, vulnerability data, and security metrics to prioritize the entities and threats with the greatest potential business impact. Accelerate the identification of critical users and assets that may pose a risk to the organization. (coming soon)
Exposure Analytics automatically collects and correlates data from your existing sources to continuously discover and map all assets, users, and their relationships across your environment. It then provides real-time visibility, detailed analysis, and easy-to-use visualizations, empowering security teams to quickly identify risks and investigate incidents. Customers can get started by navigating to Entity discovery under the Exposure Analytics section in Splunk Enterprise Security configuration management and start adding discovery sources.
Exposure Analytics collects and evaluates (through logic) field values related to assets and identities, such as IP addresses, MAC addresses, asset types, user names, titles, and emails. It also keeps track of discovery activity over time, to record changes in attribution (for example, an IP address may be linked to different assets or users at different times). Importantly, it does not collect payload data or sensitive communications; only the metadata necessary to identify and contextualize each entity is gathered.
Exposure Analytics enhances and empowers key capabilities within Splunk Enterprise Security (ES) by providing rich entity context for findings, detections, UEBA, and SOAR workflows. It also helps to transform raw security event log data into entity-aware intelligence, amplifying the value you get from Splunk ES. It enables deeper insights, effective automation, and faster, more accurate investigations across your security operations.
This is a core capability of Splunk Enterprise Security. It is included in the license for all Enterprise Security customers at no additional cost.
The AI-powered SecOps platform that unifies the best in-class SIEM, SOAR, UEBA, threat intelligence, and detection engineering into a seamless TDIR experience.
The market-leading SIEM that allows comprehensive visibility, empowers accurate detection with context, and fuels operational efficiency.
© 2005 - 2026 Splunk LLC All rights reserved.