Splunking Microsoft Azure Audit Data
Tips & Tricks Jason Conger
What are we collecting?
This update adds a new modular input to your Splunk environment:
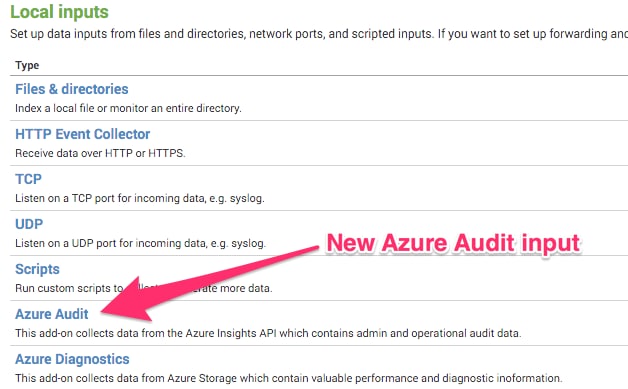
This modular input grabs data using the Azure Insights Events API.
How to use the Azure Audit data
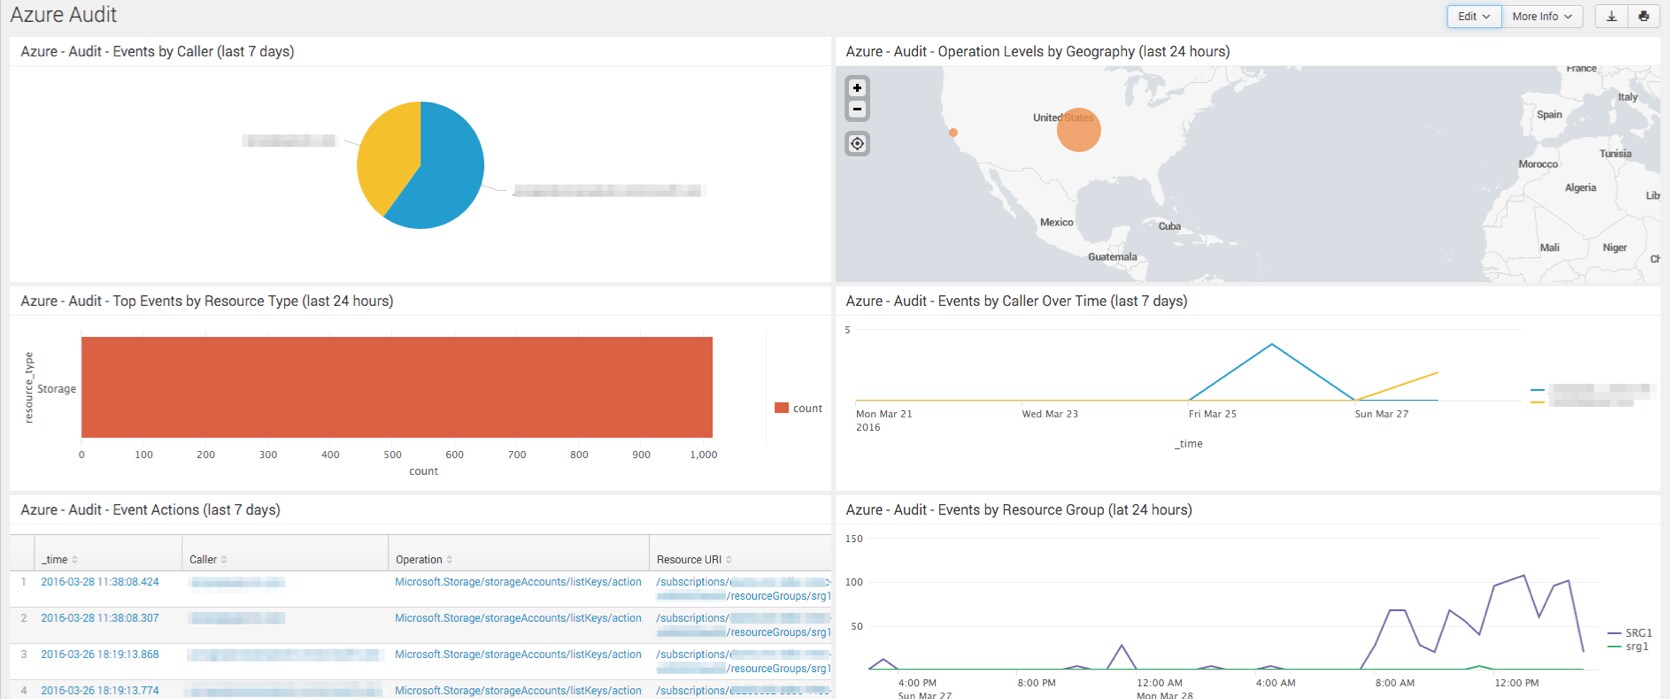
There are several new prebuilt panels included in the add-on to get you started:
Azure – Audit – Event Actions
Azure – Audit – Events by Caller
Azure – Audit – Events by Resource Group
Azure – Audit – Operation Levels by Geography
Azure – Audit – Top Events by Resource Type
Setting up the Azure Audit input
The Azure Insights Events API is a REST endpoint and requires a little bit of setup on the Azure side. An Azure Active Directory application must be set up and a few key pieces of information must be supplied to the modular input. Don’t worry though, there are step-by-step instructions provided in the docs folder in the add-on.
What is coming next?
The next integration slated to roll into this add-on is Azure Network Security Group logs – meaning network flow, load balancers, and network security group activity. Stay tuned…
Related Articles

Sending binary data to Splunk and preprocessing it