From the SecOps Kitchen: Why Operators of Essentials Services Need to Prepare Now
Security Matthias MaierHey there,
The European Union Agency for Cybersecurity (ENISA) has recently published its NIS Investment report - a survey conducted on European organisations identified as Operator of Essentials Services (OES) and Digital Service Providers (DSP).
What The Future In Security Operations Demands
The report’s focus leads mainly on technology investments as well as security skills.
Combine this with the skills that are increasing in value. Gone are the days when security officers and SOC teams would receive an award for picking up the phone, calling a software or service provider and waiting for the provider to deliver.
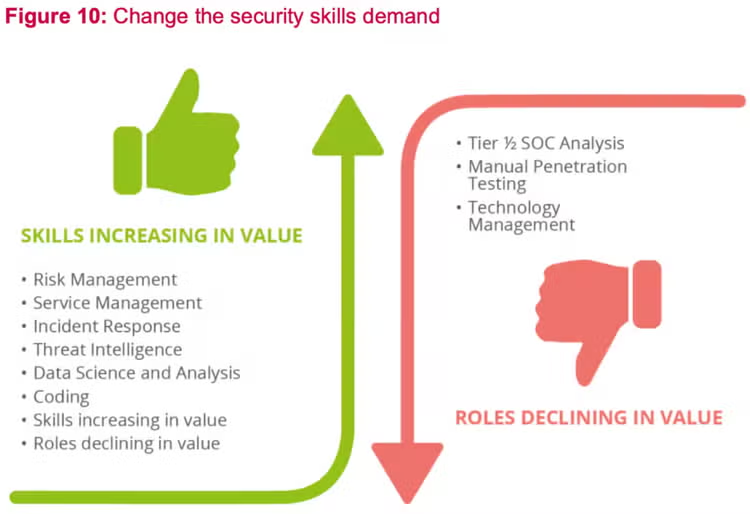
Source: ENISA NIS Investments Report, 11th of December 2020
The SecOps kitchen’s star dishes are the reserve of the cyber teams that truly deliver cybersecurity and develop skills that enhance security. Their processes start at risk management, through incident response, and move all the way to data science and analysis.
SecOps Teams Need to Plan and Build Their Kitchens Now
It isn’t the threat landscape alone that will force IT and security decision makers into building their own SecOps kitchens, but also a steady increase in regulatory requirements, including supply chain implications of customers. The fight for security chefs, skilled in the arts of risk management, incident response, threat intelligence as well as data science and analysis has begun already. You will need to ensure that your security kitchen is always kept well oiled and doesn’t show any signs of improper handling. This is especially crucial in the event that an internal or external client drops in to visit.
Inside the Security Kitchen - Master Chef Recipe
How does life at a security kitchen look like? What ingredients are needed to cook the perfect dish? How can you be agile and map technical security activities back to the overall goal to reduce the business risk and become cyber resilient while being sensitive to costs and FTE needs at the same time? According to ENISA, as of 2020, Information Security FTEs represent 5,6% of total IT FTEs.
Among our many live demos during one of our one-hour webinars, we demonstrated what it takes to cook the perfect dish in a SOC. We started by understanding the risk surface from a risk management perspective. We then began to select the right ingredients for detection and added the secret sauce for a smarter alert prioritization and response. All of this across multi cloud providers and on prem environments.
Watch the on-demand webinar: "The Security Master Chef: A Visibility and Response Recipe".
Inside Other Security Kitchens Across EMEA
If you have found inspiration on how to implement and operationalise use cases, you might also be wondering what all of this looks like to other firms, what they are doing, how they’re doing it.
Join our upcoming webinar and hear from our security experts about what we’ve learned in 2020 from leading SOC teams at Norlys, GE Digital, Siemens, Bank of England, Skyscanner and Saudi Aramco.
Sign up for our webinar “5 Security Modernization Stories: What Our Customers Taught Us In 2020”!
Related Articles
Tales of a Principal Threat Intelligence Analyst
Splunk SOAR Playbook of the Month: Splunk Attack Analyzer Dynamic Analysis