Shifting Mindsets: Modernizing the Security Operations Center
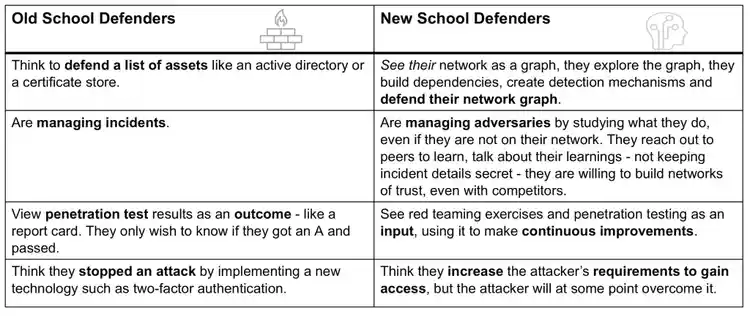
Security Matthias MaierA concept from Microsoft’s Threat Intelligence Center, presented by John Lambert caught my attention as I recently reviewed some of the MITRE ATT&CKcon sessions. His speech was about advancing InfoSec towards an open, shareable, contributor-friendly model of speeding up InfoSec learning. John researched how certain defenders have been highly successful in defending their networks, particularly where some others had been in the news for failing many times before. In doing so, he found that although many defenders operate in a similar way, what the successful security guys (advanced defenders) vs. the less successful security guys (traditional defenders) had in common was “a different kind of mindset’.
Here’s the difference between ‘old school’ and ‘new school’ defender mindsets:
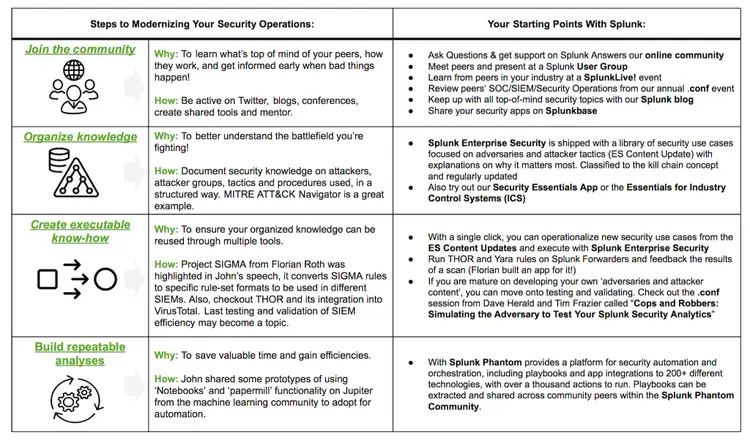
As you can see from the above, we’re here to help at Splunk! Whether you’re starting to build a centralized log management platform for security investigations, looking to optimize your existing SIEM System, or want to gain efficiencies in your Security Operations Center environment - we can offer a helping hand. Spoilt for choice of where to start? Why not check out our What’s New in Splunk Enterprise Security Webinar, and learn how automation works in Cyber Security in our IS YOUR SOC SOARING OR SNORING? Webinar.
Best
Matthias
Related Articles
Splunk Named a Leader in The Forrester Wave™: Security Analytics Platforms, Q4 2022
FIN7 Tools Resurface in the Field – Splinter or Copycat?