LOGGING
Bring logs into observability
Explore, visualize, and alert on logs alongside metrics and traces in one Splunk Observability Cloud experience.
CHALLENGE
Fragmented log workflows slow every investigation
When logs live apart from metrics and traces, engineers swivel between tools to understand system health. Separate consoles, identities, queries, dashboards, and alerts fragment context and slow response. Teams need unified access to logs without abandoning existing Splunk data or observability workflows.
SOLUTION
Choose your path to unified logs

Start with Observability Logs
Bring logs natively into Observability Cloud with integrated retention and governance.

Connect existing Splunk logs
Use Log Observer Connect with logs in Splunk Cloud Platform or Splunk Enterprise.

Act on logs in one experience
Explore, visualize, and alert on logs alongside metrics, events, and traces.
Lead with native logs from Observability Logs
Observability Logs brings logs natively into Splunk Observability Cloud for new observability deployments. Search recent logs, retain older data in the Machine Data Lake, and promote selected historical data for ad hoc investigation.
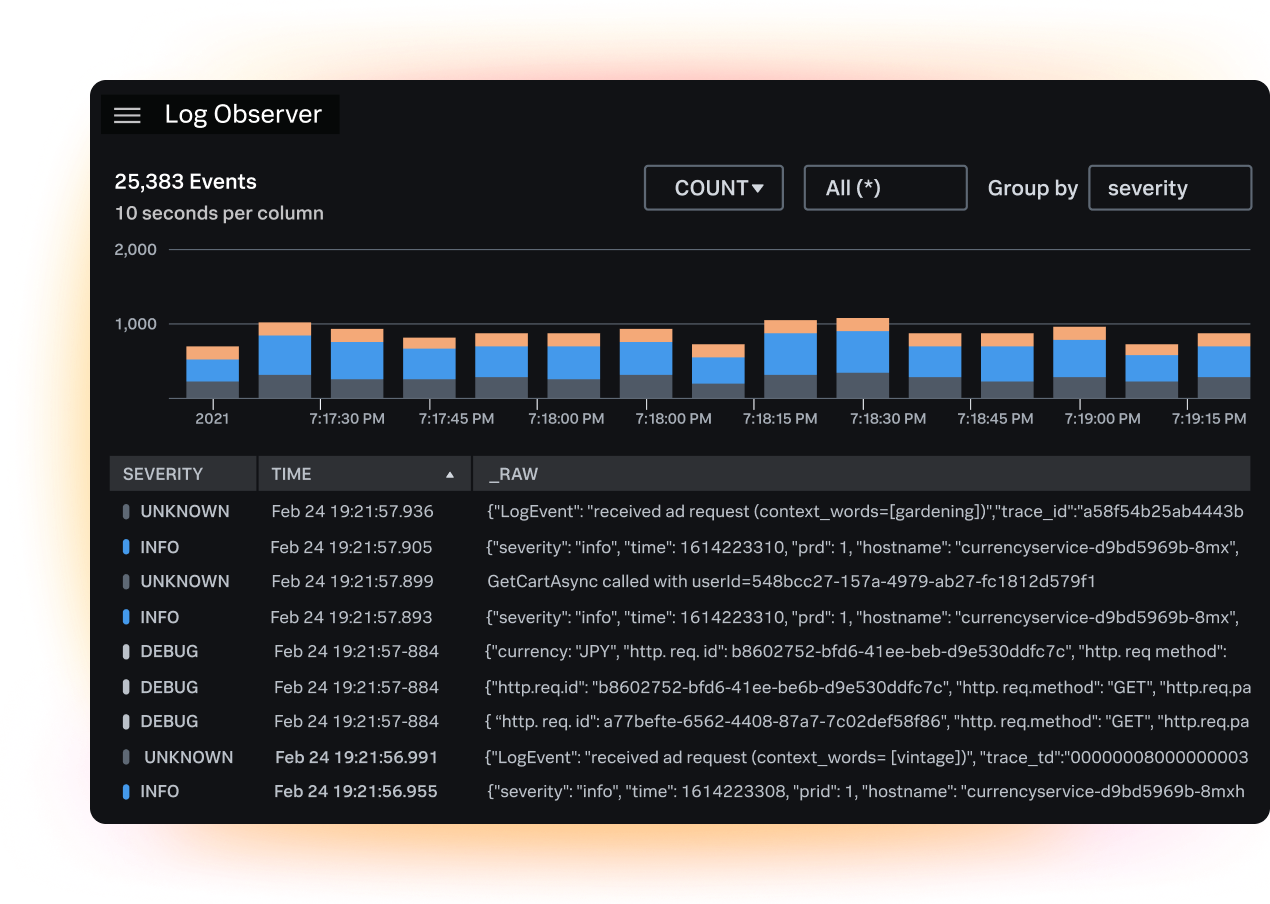
Connect the Splunk logs you already have
Existing Splunk Cloud Platform and Splunk Enterprise customers can use Log Observer Connect to analyze their logs in Observability Cloud. Add log context to metrics and traces while keeping Splunk Platform as the system of record.
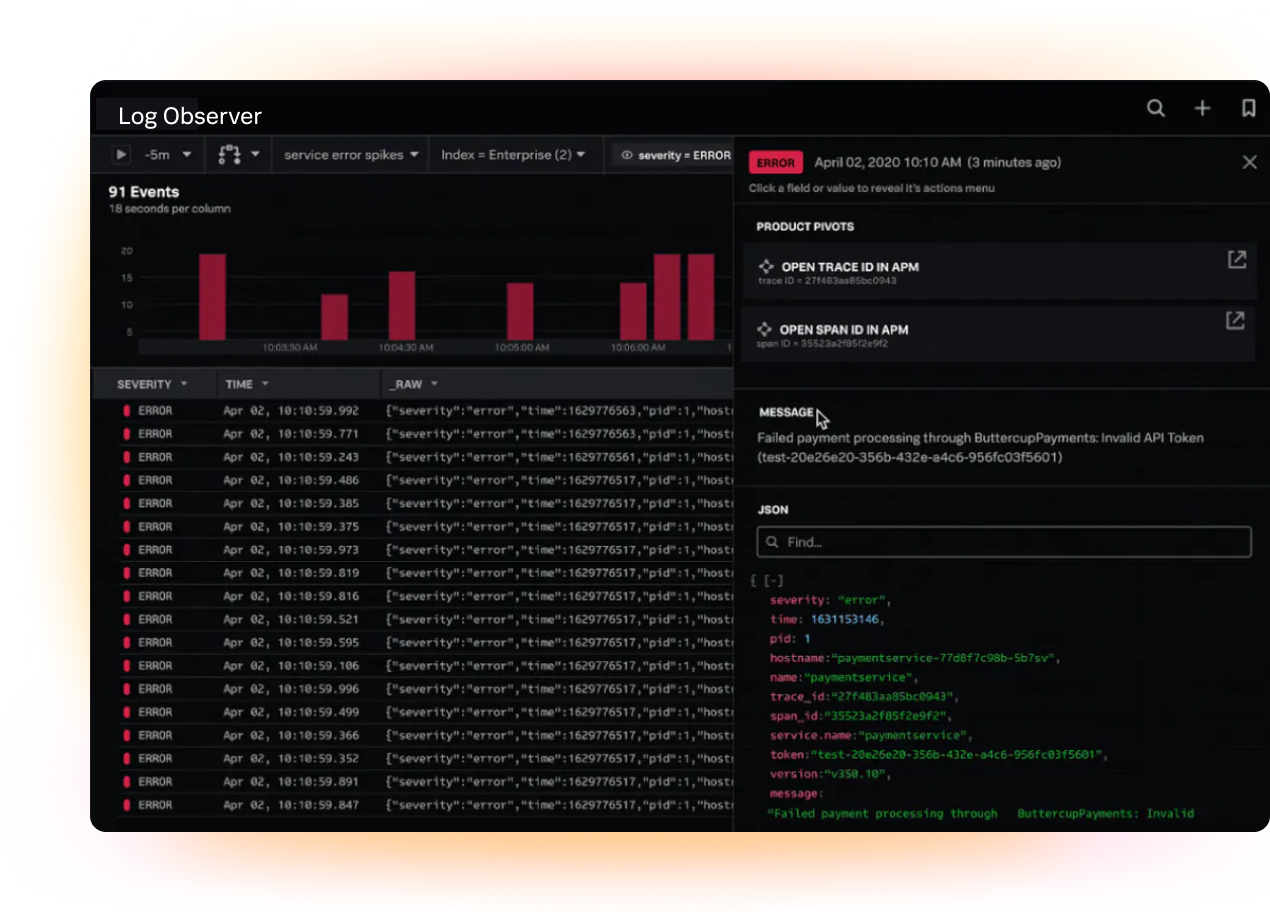
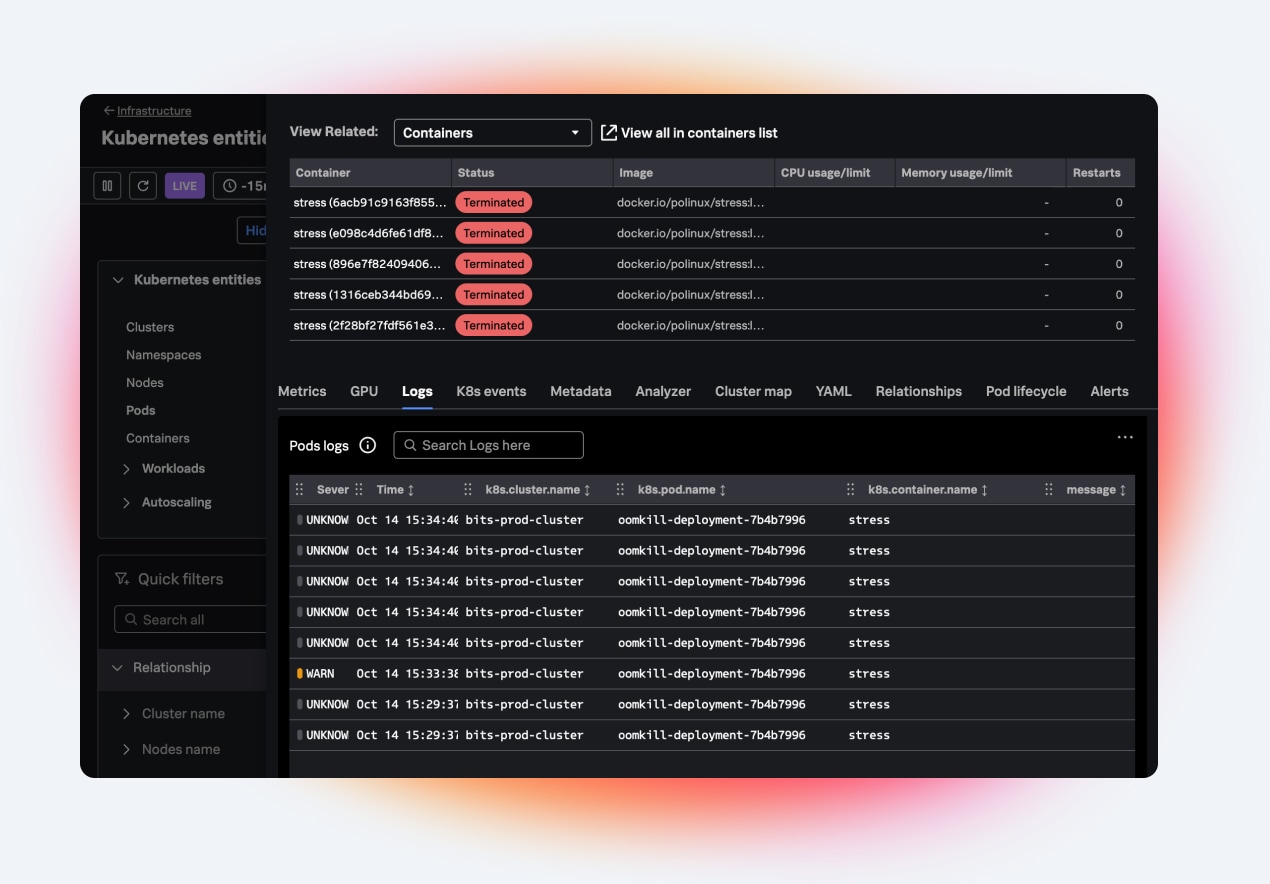
Investigate logs in Log Explorer
Use point-and-click, natural language, SPL to inspect events and refine searches. Correlate logs with infrastructure, APM, RUM, Synthetic Monitoring, service, and incident context, then move directly into charts or alerts.
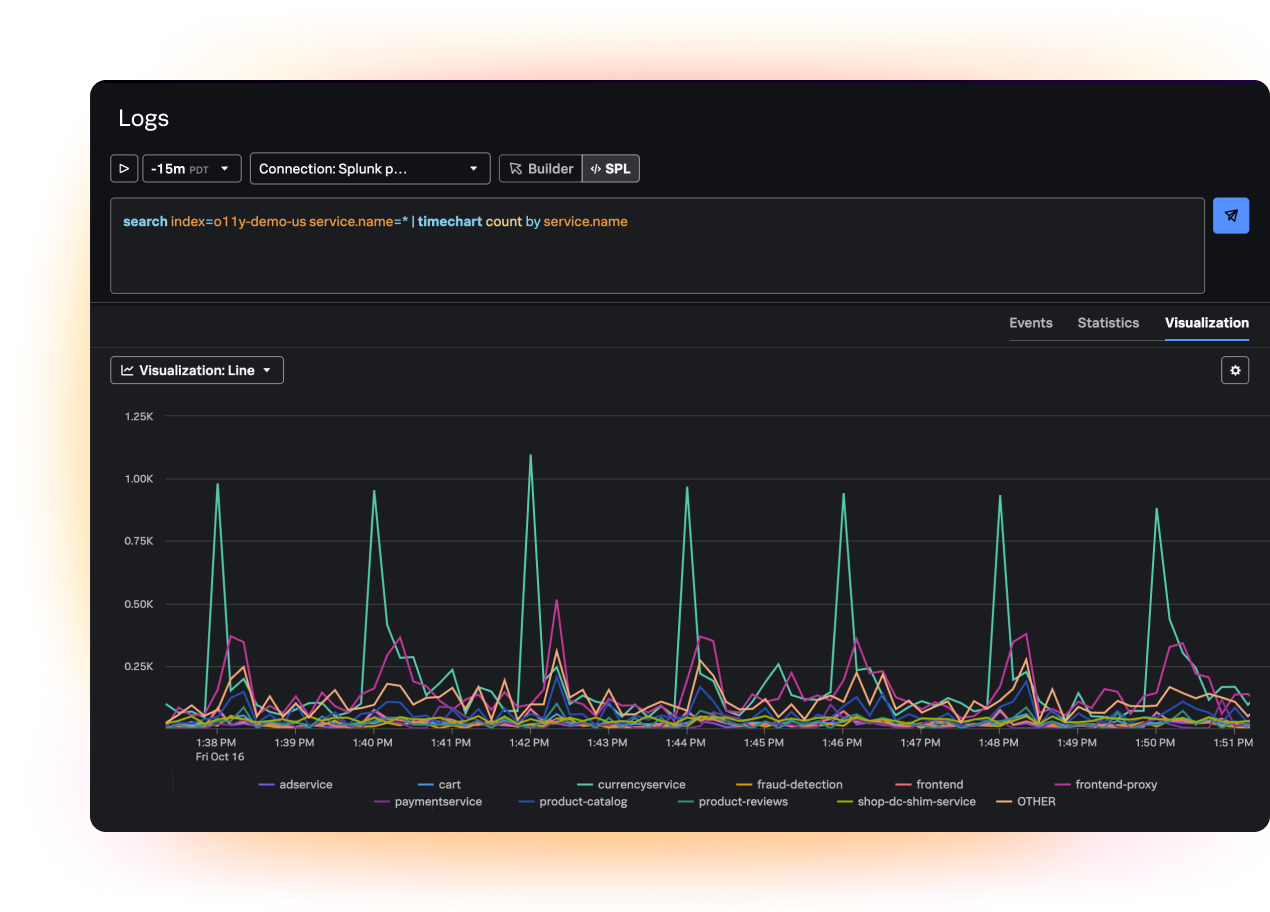
Build log-based charts in modern dashboards
Create log-based charts directly in Splunk Observability Cloud dashboards. Use SPL to visualize log data beside metrics, events, and traces — giving teams a unified view of system health without switching consoles.
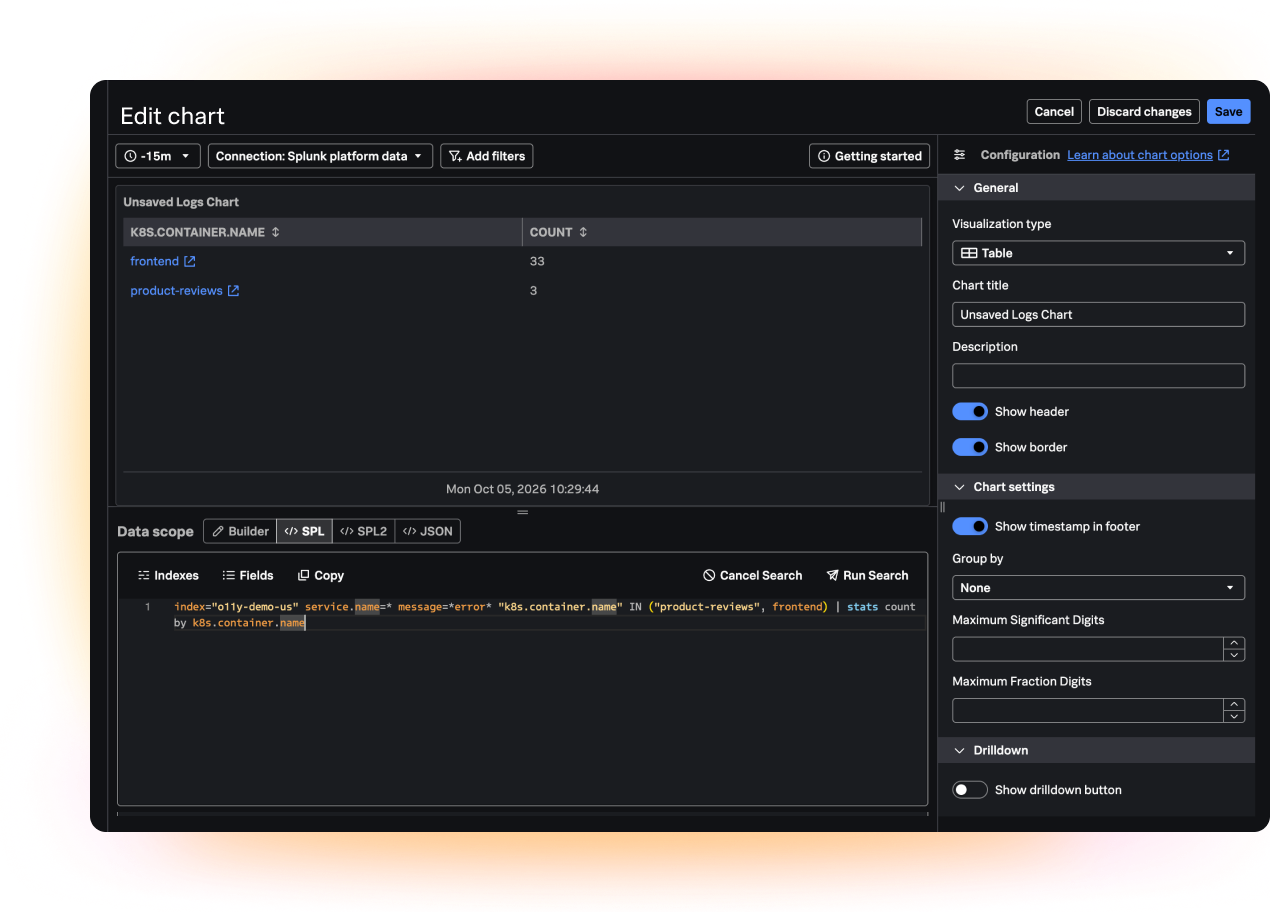
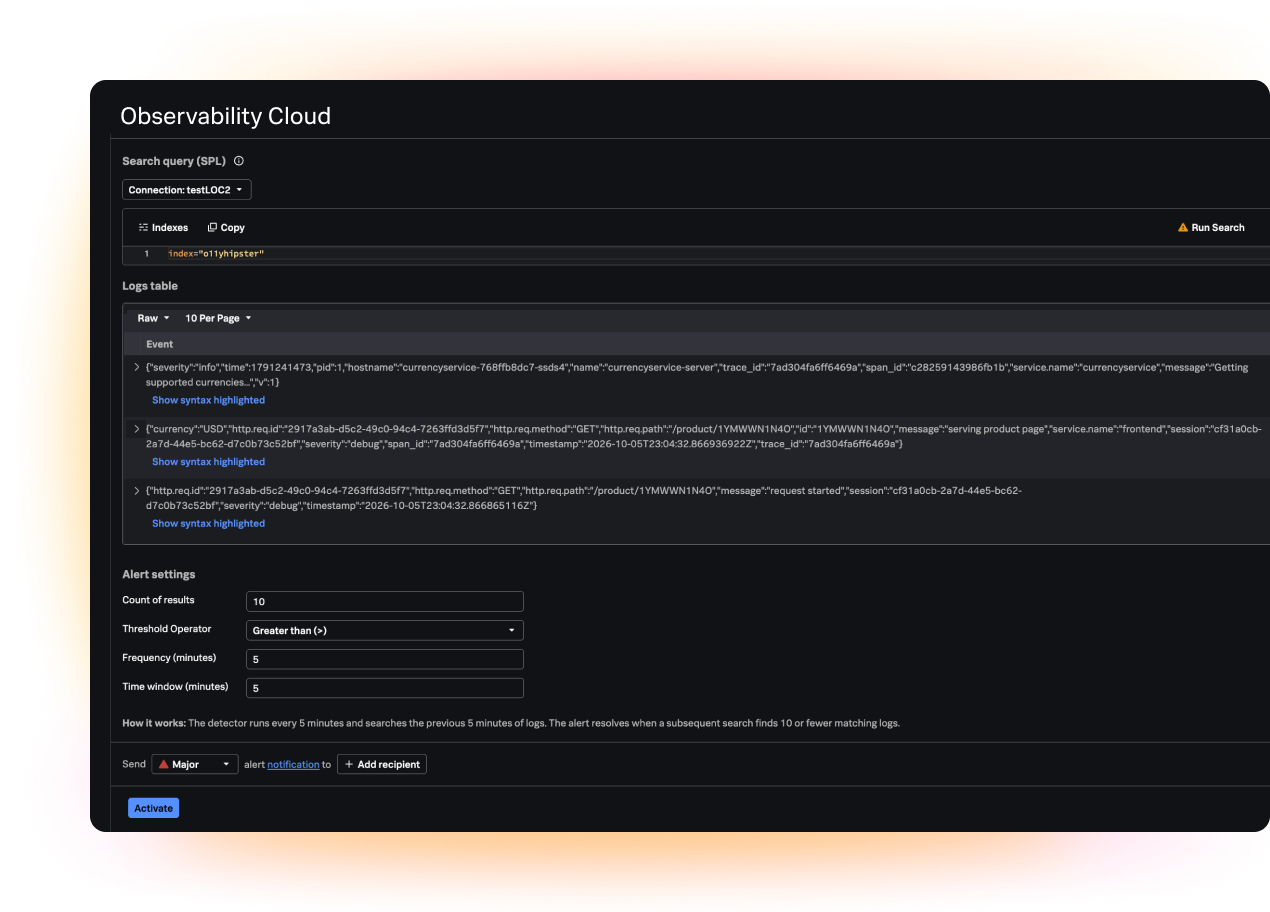
Detect issues with log-based alerts
Create and manage search-based log alerts in Observability Cloud. Use AI-driven SPL assistance and cross-signal context to build precise, actionable alerts, reduce alert fatigue, and accelerate detection and response.
Features
Search, filter, and analyze log data at scale
Tap into industry-leading log management and analytics in Splunk Observability Cloud.

See data in context
Visualize the real-time metrics and traces for a specific log event in the same interface for more context.

No code, no problem
Perform queries or searches in a codeless and intuitive interface with pre-packaged dashboards and filters.

Report key insights in custom dashboards
Add log-based charts to customized dashboards for better metrics-based monitoring and faster root cause analysis.
Open logs in Splunk Search
With one click, transfer the logs you see in Observability Cloud into Splunk’s Search and Reporting for your more advanced log analyses.
Optimize your storage
Store unused log data in 3rd party locations (IaaS or SaaS) to reduce indexed capacity and storage costs.
Are you a current Observability Cloud customer looking for learning resources?
Check out our Observability Learning Path on Splunk Community, with curated content organized by skill level.
CUSTOMER STORY
Rappi Fixes Issues 90% Faster During a 300% Surge in Orders
A single dashboard provides data for engineering, DevOps, site reliability engineering, SecOps, peer engineering and microservices, operations and business metrics. If something happens at Rappi, and we don’t see it on our Splunk dashboard, it’s actually not happening at all.


Splunk AppDynamics
Observe and secure your hybrid and on-prem applications across every environment.
Splunk Infrastructure Monitoring
The only real-time, analytics-driven multicloud monitoring solution for all environments.
Splunk Application Performance Monitoring
Full-fidelity tracing and always-on profiling to enhance app performance
Splunk Real User Monitoring
Add the only full-fidelity, end-to-end visibility solution for end-user experience.
Splunk Synthetic Monitoring
Go beyond basic uptime and performance monitoring for better digital experiences.