Security
Splunk Security Orchestration, Automation, and Response (SOAR)
Orchestrate security workflows and automate tasks in seconds to empower your SOC, work smarter, and respond faster.
Security
Orchestrate security workflows and automate tasks in seconds to empower your SOC, work smarter, and respond faster.
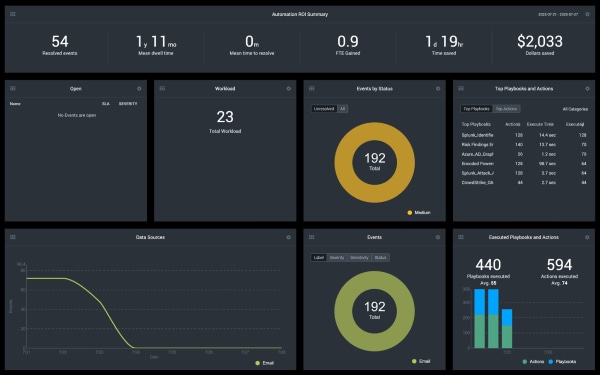
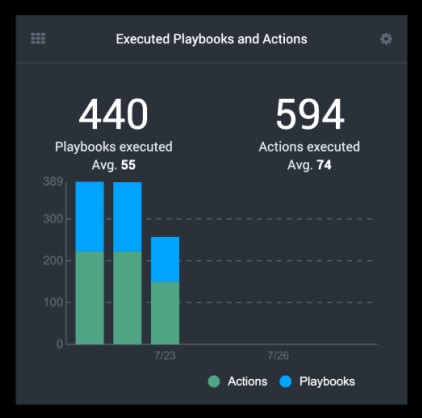
Splunk SOAR is designed to integrate and enhance your security operations seamlessly. It orchestrates your security stack by connecting with 300+ third-party tools and supporting 2,800+ automated actions.
Splunk SOAR can streamline your response and automation processes by consolidating alerts and data from the various tools in your environment, ensuring timely and prioritized responses.
Seamlessly orchestrate across your environment
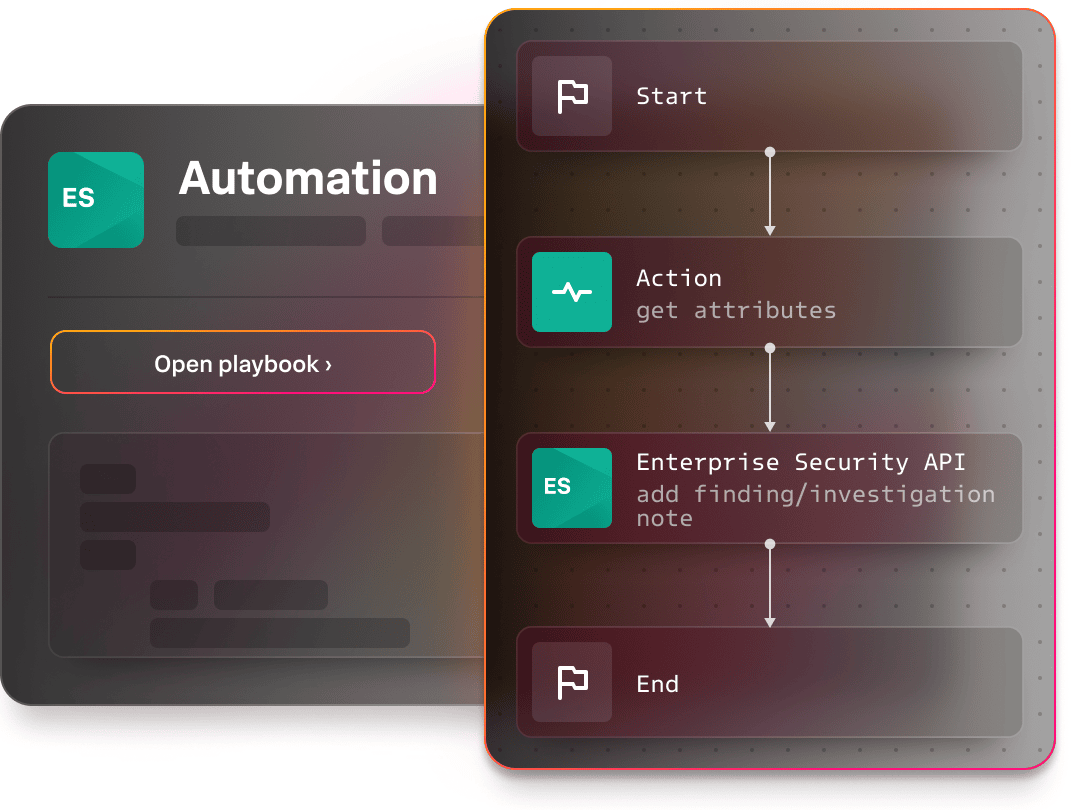
Splunk SOAR empowers users to easily automate security tasks with playbooks that can be customized to fit your needs. Splunk SOAR features a wide variety of prebuilt playbooks, which leverage the MITRE ATT&CK and D3FEND frameworks, are all aligned to foundational SOC tasks, and help ensure you can automate everything from small steps to end-to-end use cases.
Combine infrastructure orchestration, playbook automation, built-in threat intelligence, and full-fledged integration with Splunk Enterprise Security to streamline your security processes and tools.

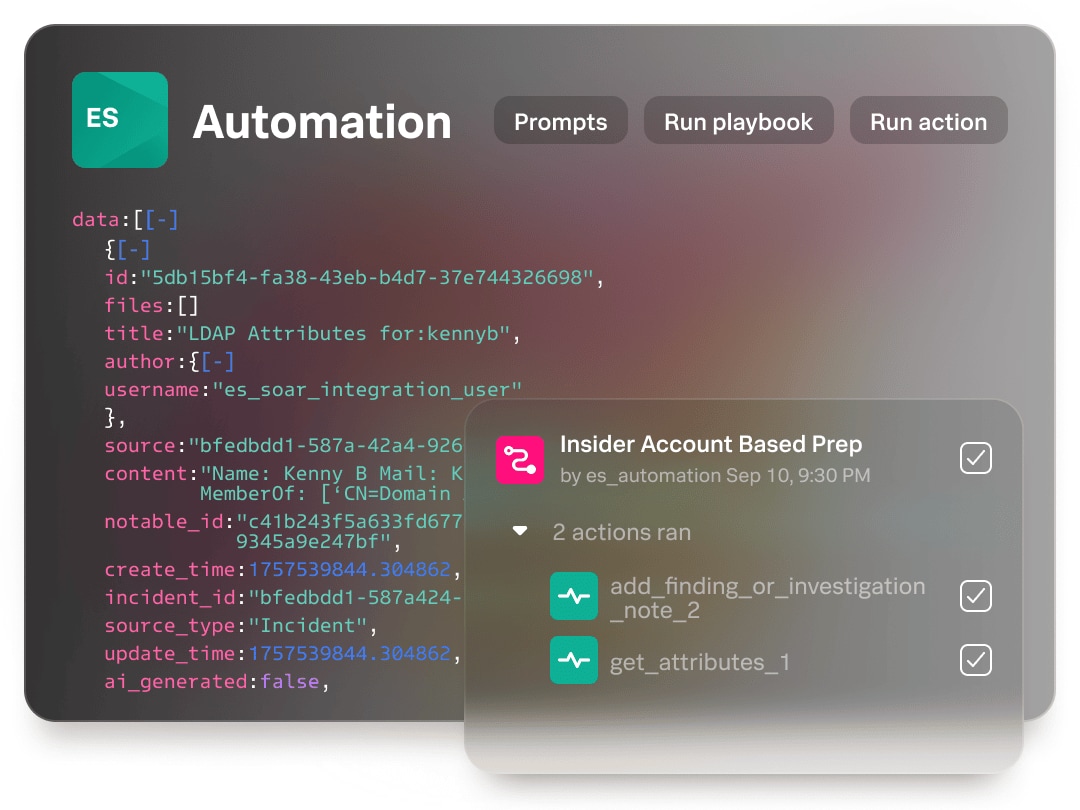
Execute actions across security and IT tools in seconds instead of hours. Splunk SOAR comes with a plethora of playbooks to help you tackle the use cases that matter most.

Splunk SOAR integrates across 300+ third-party tools and supports 2,800+ automated actions. Connect and coordinate complex workflows across your teams and tools, so you don’t need to rip and replace your existing stack.

Whether you’re new to coding or an expert, Splunk SOAR’s Visual Playbook Editor simplifies the playbook creation process by allowing you to assemble custom workflows with prebuilt code blocks while still providing intuitive editing options.

Whether you're using custom templates or industry standards for incident response, Splunk SOAR facilitates task segmentation, assignment, and documentation, ensuring a cohesive and collaborative investigative process.

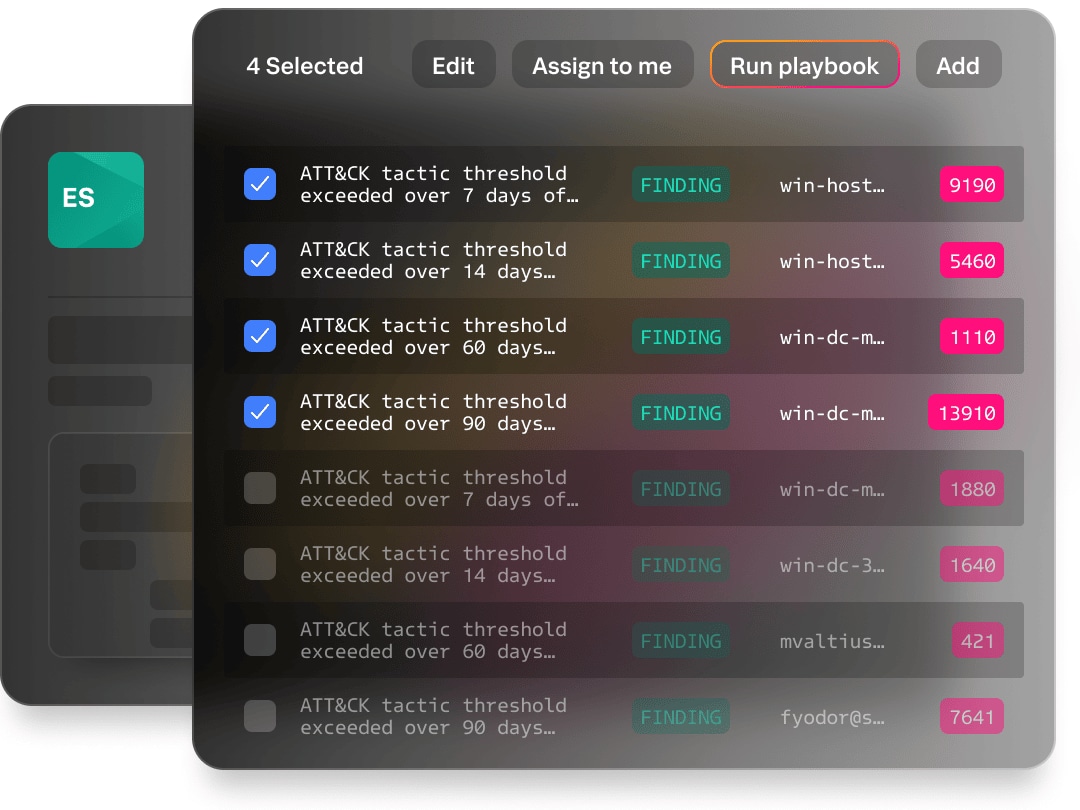
Splunk SOAR’s investigation panel helps you prioritize what threats to act on, all from one location. Additionally, the built-in threat research and insights from the Splunk Threat Research Team help you make informed decisions and stay ahead of threats.

Splunk SOAR can be deployed via the cloud, on-premises or hybrid. Splunk SOAR capabilities can also be leveraged by your Splunk Enterprise Security deployment for a seamlessly integrated unified workflow experience (Splunk SOAR subscription required).
Novuna has used Splunk SOAR to manage and contain 80,000 events, saving more than $500,000 as a result of licensing savings, increased user efficiency, and reduced on-call hours - within 8 months.
With Splunk SOAR and Splunk Attack Analyzer, we're resolving phishing alerts 90% faster.
We now have visibility into all of our tools and resources, whether they’re homegrown or third-party applications. That information raises security consciousness and informs the actions we take across the business.

Streamline your threat detection, investigation, and response with Enterprise Security — a unified TDIR platform with integrated SIEM, SOAR, UEBA, and agentic AI.
© 2026 Cisco Systems, Inc. and its affiliates. All rights reserved.