/en_us/blog/leadership/splunk-by-cisco-brings-agent-roi-to-aws-marketplace

Splunk Blogs

Observability

Artificial Intelligence

Cisco Data Fabric

Latest Articles

How to Splunk Data from a Raspberry Pi – Three Easy Steps!
Industries
5 Minute Read

How to Splunk Data from a Raspberry Pi – Three Easy Steps!

Last week we announced a release of our Universal Forwarder for Linux ARM (Raspberry Pi) which greatly simplifies the process of taking any data from a Raspberry Pi including GPIO or other connected sensors and attached shields and sending that data to Splunk. While this task was not impossible before, the process involved manual streaming of data to the Splunk API. Using a Universal Forwarder you can take advantage of Splunk’s end to end data distribution mechanisms with no need to understand or develop against Splunk’s API.
Introducing: The Splunk App for Okta
Security
2 Minute Read

Introducing: The Splunk App for Okta

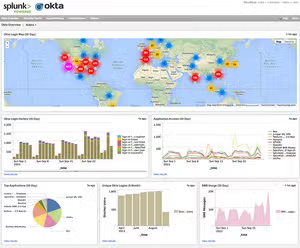
The Splunk App for Okta connects to the Okta events API and returns data in a CIM-compatible format for Splunking.
Windows Event Logs in Splunk 6
Tips & Tricks
2 Minute Read

Windows Event Logs in Splunk 6

Quite a while ago I wrote a blog post entitled The Splunk App for Active Directory and How I tamed the Security Log. It detailed how to limit the amount of data that was going into the Splunk index through filtering.
Export Search Results with PowerShell
Tips & Tricks
2 Minute Read

Export Search Results with PowerShell

A while back, I wrote an introduction to how you could play with our C# SDK from PowerShell. And just the other day, Adrian wrote a post talking about how you could export really large result sets to CSV, using the REST API.
Monitoring Scheduled Tasks with PowerShell
Tips & Tricks
4 Minute Read

Monitoring Scheduled Tasks with PowerShell

I did the unthinkable yesterday. I combed through my posts for non-spam comments. I apologize to everyone whom I didn’t answer – we get a lot of comment spam that I have to wade through when I do this. However, there were a couple of requests in there for future topics and I’ll try and cover those requests in the next few weeks.
Exporting Large Results Sets to CSV
Tips & Tricks
2 Minute Read

Exporting Large Results Sets to CSV

You want to get data out of Splunk. So you do the search you want and create the table you want in the search app. The results are hundreds of thousands of rows, which is good.
Detecting Fraud
Security
5 Minute Read

Detecting Fraud

I sometimes get asked if Splunk can detect fraud. The answer is yes, but the question is broad and needs an understanding of the situation that needs to be detected before making a generalization.
An easy way to generate sample data
Tips & Tricks
3 Minute Read

An easy way to generate sample data

Have you ever had a Splunk project that required a data feed, but for whatever reason it wasn’t practical to tap into the source itself? Examples of this could be;
Audit File Access and Change in Windows
Tips & Tricks
3 Minute Read

Audit File Access and Change in Windows

One of the bigger problems that we come across is auditing of file systems – specifically, you want to know who read, modified, deleted or created files in a shared area. This is not an unreasonable task, but it is different in every single operating system. Windows has built-in facilities for doing this. We just need to do a few things to get the information into Splunk.