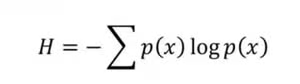/en_us/blog/leadership/splunk-by-cisco-brings-agent-roi-to-aws-marketplace

Splunk Blogs

Observability

Artificial Intelligence

Cisco Data Fabric

Latest Articles

Intro to Python Frameworks Part 2 – Full-Stack vs. Micro Framework
Observability
6 Minute Read

Intro to Python Frameworks Part 2 – Full-Stack vs. Micro Framework

An overview of some of the top frameworks in each category, the features that make them unique, and the reasons you should put them to work in your next application. First, let’s examine full-stack followed by micro-stack.
Splunk Logging Driver for Docker
Tips & Tricks
3 Minute Read

Splunk Logging Driver for Docker

With Splunk 6.3 we introduced HTTP Event Collector which offers a simple, high volume way to send events from applications directly to Splunk Enterprise and Splunk Cloud for analysis. HTTP Event Collector makes it possible to cover more cases of collecting logs including from Docker. Previously I blogged on using the Splunk Universal Forwarder to collect logs from Docker containers.
Saving money with IoT at home!
Tips & Tricks
3 Minute Read

Saving money with IoT at home!

I recently blogged about how Udo, a member of the EMEA technical services team, is monitoring his smart home. Inspired by his use case I started to investigate if I too could collect data from my heating system to do a similar sort of analysis.
A Technical Deep Dive into Python
Observability
6 Minute Read

A Technical Deep Dive into Python

In this article, you will gain a better understanding of Python, why it is so popular among programmers, its basic functionality and a few of its drawbacks.
Hackers are already in your environment – spot them with THOR and Splunk!
Security
2 Minute Read

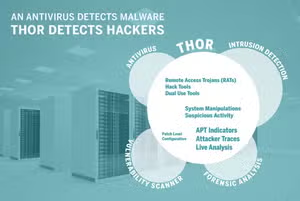
Hackers are already in your environment – spot them with THOR and Splunk!

You probably already know about antivirus scanners, IDS Solutions, vulnerability scanners as well as sandbox execution systems like FireEye, the WildFire service from Palo Alto or ThreatGRID from Cisco. However, one of the latest tools, “THOR“, is different.
Monitor your own Smart Home – three top tips from Splunk
Tips & Tricks
2 Minute Read

Monitor your own Smart Home – three top tips from Splunk

One of the great things at Splunk is that there are so many devices you can collect data from and make something meaningful out of.
IoT and Flying Ponies at .conf 2015
Tips & Tricks
1 Minute Read

IoT and Flying Ponies at .conf 2015

One of the coolest demos I witnessed at Splunk .conf 2015 was the one by Nate McKervy. The reasons this demo was so cool is 1) it was live, 2) it involved audience participation, and 3) it involved shooting stuffed ponies out of an air cannon. This article will explain a little more of what was going on under the covers.
Random Words on Entropy and DNS
Security
4 Minute Read

Random Words on Entropy and DNS

Capturing Akamai Data with Splunk
Tips & Tricks
3 Minute Read

Capturing Akamai Data with Splunk

Monitor Akamai data in Splunk, cloud service SLAs, visibility of apps, security incidents/events, Cloud Monitor real-time HTTP feed delivers data in JSON format