/en_us/blog/leadership/splunk-by-cisco-brings-agent-roi-to-aws-marketplace
Featured Articles
displayMode
carousel
filter
paths
paths
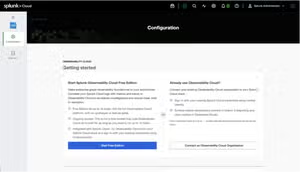
Observability at Your Fingertips Directly From Splunk Platform—for Free
Introducing the Splunk Observability Cloud App
Splunk Blogs
Observability
displayMode
carousel
filter
paths
paths
Show What Your Agents Are Worth With Tokenomics
We are launching Tokenomics by Splunk soon to be available on AWS Marketplace.
Artificial Intelligence
displayMode
carousel
filter
paths
paths
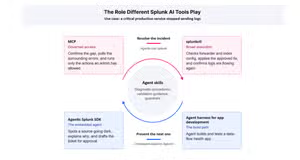
Splunk MCP Server 2.1: Enhanced Token Management and OAuth Integration for AI Agent
What changed in Splunk MCP Server 2.1 and three ways to connect an agent.
Cisco Data Fabric
displayMode
carousel
filter
paths
paths
/en_us/blog/platform/splunk-platform-innovations-cisco-data-fabric-generally-available
/en_us/blog/platform/escaping-the-cloud-walled-garden
/en_us/blog/platform/machine-data-lake-and-catalog
/en_us/blog/platform/making-machine-data-easier-to-onboard
/en_us/blog/platform/a-general-purpose-lakehouse-is-not-enough-for-machine-data
/en_us/blog/platform/escaping-the-cloud-walled-garden
/en_us/blog/platform/machine-data-lake-and-catalog
/en_us/blog/platform/making-machine-data-easier-to-onboard
/en_us/blog/platform/a-general-purpose-lakehouse-is-not-enough-for-machine-data
Escaping the Cloud Walled Garden
Three Critical Gaps in Multicloud Machine Data—and How Cisco Data Fabric Closes Them