Digital Resilience in the Agentic Era at Splunk .conf26
Leadership Mangesh PimpalkhareKey takeaways
- Join Splunk .conf26 in Denver September 14-17 to explore digital resilience, AI, security, observability, and the latest Splunk innovations.
- Hear real-world lessons from customers, practitioners, partners, and Splunk leaders through keynotes, technical sessions, workshops, and panels.
- Discover how Cisco Data Fabric and the Splunk Platform make machine data AI-ready, helping organizations gain cross-domain insights and enable agentic operations.
The agentic era is no longer a promise on the horizon. It’s running in production, at scale, in the environments you depend on every day. And once a year, we bring the people driving that shift into the same room. That’s what Splunk .conf is about: four days where our customers, end users, partners, SplunkTrust members (you’ll spot their signature fezzes), and Splunk’s own leaders come together to discuss the imperative of digital resilience, the innovation needed to deliver it, and the connection we all need to succeed in the agentic era.
Last fall, we introduced Cisco Data Fabric powered by the Splunk Platform as the data foundation for successfully implementing AI at scale. Since then, we’ve delivered solutions to our customers that enable them to manage the complexity of scattered, disconnected data to get real value from their AI investments. We released features like Federated Search across multiple data lake alongside Machine Data Lake, Catalog, and Agent Launchpad. These capabilities are key to the foundation we built to make machine data AI-ready, so customers can be proactive and predictive by leveraging Agentic operations which enables teams to focus on driving business outcomes rather than reactive firefighting.
And that was only the beginning.
I’m looking forward to seeing you at .conf26, where we’ll convene in Denver, Colorado, on September 14-17, to sharpen skills, hear first-hand customer stories, and explore the latest innovations across the Splunk platform, security and observability. Just as importantly, we’ll hear from our community of practitioners, customers, and partners on their successes, challenges, and lessons learned.
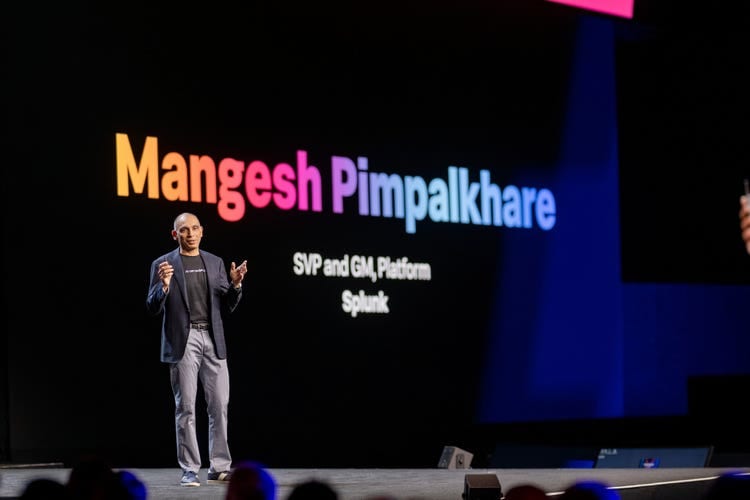
Powering the Trusted Agentic Enterprise
I’m most excited to hear from the practitioners doing the work: the engineers building detections at 2 a.m., the SOC leads working with Agents to defend a global brand, and the architects bringing order to complex environments. Every year, we spend as much time as we can listening to them, unfiltered, about what’s working and what isn’t. That feedback doesn’t just inform our roadmap. It sharpens it.
You’ll also hear from industry-leading customers like Atlassian, Autodesk, BMO, and Hyatt, who will share the successes, challenges, and insights that will help you on your own digital resilience journey.
On the mainstage at .conf26, we’ll discuss how the insights you shared last year shaped the next wave of Splunk.
- Welcome Keynote: Jeetu Patel, President and Chief Product Officer, Cisco and Kamal Hathi, SVP and GM, Splunk Business Unit at Cisco, will reveal our latest announcements and vision for the future.
- Product Keynote: Kamal and I, along with my Security and Observability peers, will guide you through what's next for Splunk, and demonstrate how Cisco and Splunk are delivering cross-domain insights, intelligent context, and end-to-end visibility needed to power the agentic enterprise.
- Breakout Sessions: Explore workshops, expert-led panels, and technical breakouts designed to spark new ideas and sharpen your skills.
- Splunk Pavilion: Step into the heart of the event to connect with Splunk experts and partners, get hands-on with our latest innovations, and grab your official .conf26 gear.
This year’s session catalog is grounded in real work. Attendees will get practical, hands-on experience from customers operating at massive scale, with sessions built on lessons learned in production, not just theory.
Digital resilience is not a destination you arrive at once and declare finished. It’s a practice, built through meticulous preparation, tested in real customer environments, and improved every single year by the people willing to tell us honestly what is and isn’t working.
We're coming to Denver ready to share what we’ve built over a year of hardening this foundation, shaped by a community that keeps us honest, and eager to see what we’ll learn together at .conf26.
That's the journey ahead, and we wouldn't trade it for anything. See you in Denver.
Related Articles
Splunk SOAR Playbooks: GCP Unusual Service Account Usage
Splunk Security Content for Impact Assessment of CrowdStrike Windows Outage