Recap: Splunk @ Blackhat Europe 2016
Security Matthias Maier
Splunk’s schedule was full during the briefing days. In our booth we shared the latest technology about big data analytics in security, machine learning, threat intelligence gathering and how security team’s should prepare for the future with automation.
THREAT HUNTING PRESENTATION, BUSINESS HALL
James Hanlon, Security Markets Specialist, presented in the Business Hall about how organizations should carry out threat hunting activity, including detail on what people, technology and processes are required. This also included discussion of how threat-hunting maturity develops from an initial ad hoc basis towards utilising advance machine learning capabilities.
HANDS ON THREAT-HUNTING WORKSHOP
SPLUNK DATA SCIENTISTS: AKTAION, ARSENAL
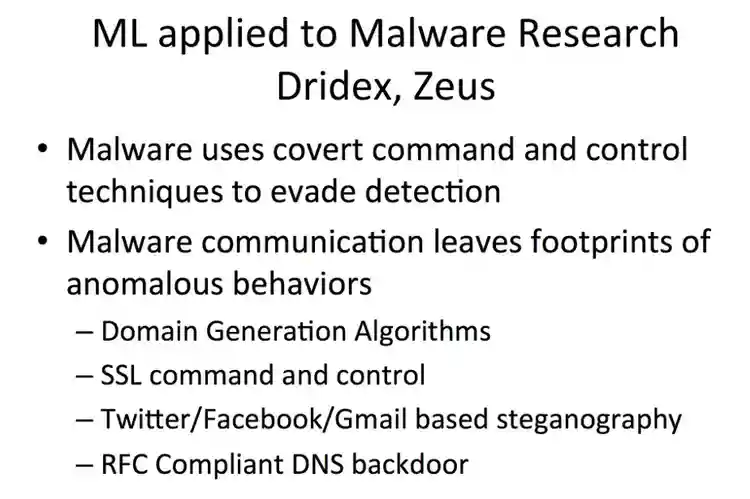
AKTAION PPT
On Friday we also had two Data Scientists from Splunk presenting in the Arsenal. Rod Soto and Joseph Zadeh presented on Crypto Ransomware, which has become a popular attack vector used by malicious actors to quickly turn infections into profits. From a defensive perspective, the detection of new Ransomware variants relies heavily on signatures, point solution posture and binary level indicators of compromise (IOC). This approach is inefficient at protecting targets against the rapid changes in tactics and delivery mechanisms typical of modern ransomware campaigns. They proposed a novel approach for blending multiple signals (called micro behaviors) to detect Ransomware with more flexibility than using IOC matching alone.
The goal of this approach is to provide expressive mechanisms for detection via contextual indicators and micro behaviors that correlate to attacker tactics, even if they evolve with time. They provided open source code that allows users and fellow researchers to replicate the use of these techniques. They concluded with a focus on how to tie this approach to active defence measures and existing infrastructure.
You can find their Presentation and Whitepapers on GitHub here. They have also published the Aktaion Tool for learning/teaching use here on GitHub.
Stay Safe and Happy Splunking,
Matthias
Related Articles
Supercharge Cybersecurity Investigations with Splunk and Graphistry: A Powerful Combination for Interactive Graph Exploration
Unveiling Splunk UBA 5.3: Power and Precision in One Package