Unveiling Splunk UBA 5.3: Power and Precision in One Package
Security Tom SmitIn the face of an ever-evolving cybersecurity landscape, Splunk never rests. Today, we're ecstatic to share the release of Splunk User Behavior Analytics (UBA) 5.3, delivering power and precision in one package, and pushing the boundaries of what's possible in user and entity behavior analytics.
Redefining the Cluster Landscape: 20 Node XL
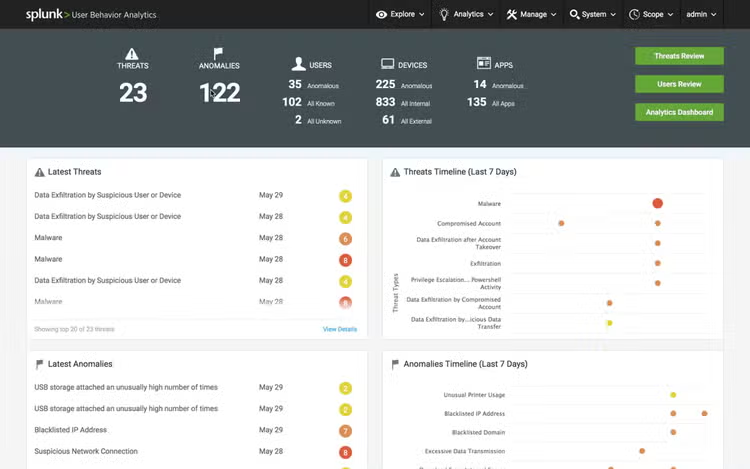
Splunk UBA is already renowned for its scalability, but with Splunk UBA 5.3, we're setting a new benchmark. Say hello to the 20 Node XL cluster. More than just an upscaled version of our classic 20 node, the XL is designed for power users. Whether you're dealing with a colossal volume of events per second (up to 160,000), managing up to 750,000 accounts, or monitoring up to a whopping 1 million devices, the 20 Node XL is your reliable powerhouse to deliver extraordinary scale and scope. Want a deep dive into the XL's offerings? Check out the Plan and Scale your Splunk UBA Deployment Manual.
Fresh Splunk UBA Models: Writing the Next Chapter in Cybersecurity
Every cybersecurity professional knows the importance of staying ahead of the curve. That’s why Splunk UBA 5.3 introduces innovative models to amplify your defense strategies:
- Lateral Movement Model: Detect potential threats trying to traverse your network horizontally, a common tactic among advanced adversaries.
- VPN Login Anomalies: With remote work becoming the norm, ensure that your VPN logins remain genuine and safeguarded.
- Time-series Model: Dive deep into patterns over time, enabling more robust anomaly detection than ever before.
Triad of Tech Upgrades: OS, Health, and Security
Consistency is key. The Splunk UBA 5.3 release supports:
- Ubuntu 20.04, carrying forward the same support as in 5.2.
- Expanded support for RHEL versions 8.6 and 8.8.
- Oracle/Linux version 8.8, upgraded from 8.6.
And for our cloud enthusiasts, the UBA 5.3.0 AMI package will soon grace AWS environments.
With Splunk UBA 5.3, we've also integrated disk utilization into the Health Monitor UI. This enhancement offers peace of mind, ensuring that your backups are always ready and waiting when you need them most.
But that's not all! We've made several security updates in UBA 5.3. Please refer to the release notes for details.
Your Next Step in Behavioral Analytics
The journey of cybersecurity is unending, with every step being crucial. With UBA 5.3, we've taken a giant leap, ensuring that you remain at the forefront of protection and insight. Eager to embrace the advancements? Dive deeper into Splunk UBA and explore how 5.3 can redefine your analytics journey!
Related Articles
Detecting Google Cloud Platform OAuth Token Abuse Using Splunk