Introducing Ingest Processor: An Evolution in Splunk Data Management
Platform Poornima DevarajSplunk is pleased to announce the general availability of Ingest Processor, a Splunk-hosted offering within Splunk Cloud Platform designed to help customers achieve greater efficiencies in data transformation and improved visibility into data in motion. Ingest Processor joins Edge Processor, launched last year, to formalize Splunk’s Data Management portfolio, where we continue to invest in a multi-tenant cloud-based architecture to autoscale in response to increased workloads, and SPL2, our next-gen data search and preparation language that offers increased flexibility to shape data - all with an eye on cost-effectiveness.
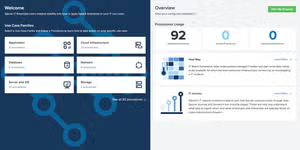
With Ingest Processor, customers can easily filter, mask, enrich and otherwise transform data at the point of ingest, before routing it to supported destinations Splunk Cloud Platform, Amazon S3 and newly, Splunk Observability Cloud. Unique to Ingest Processor is that it enables a new capability – the conversion of logs to metrics in an effort to further optimize monitoring. Plus, given that this is a Splunk-hosted service, Ingest Processor is offered at two tiers — Essentials and Premier — depending on data processed volumes per day.

Customers now have a choice of deployment model – Edge Processor for those who require more control over data before it leaves their network boundaries and therefore need to host their own infrastructure, or Ingest Processor for customers all in on cloud, and distinctly, who want Splunk to manage the infrastructure for you. Furthermore, both pipeline processors can receive data from Splunk Universal and Heavyweight Forwarders, HEC and syslog.
Check out this video to see it in action.
Availability
At launch, Ingest Processor is available on Splunk Cloud AWS Victoria stacks upgraded 9.1.2312.202. It’s also CCF compliant, but don’t fret – PCI and HIPAA compliance are roadmap items coming soon.
It’s also available in a market near you, with plans for further regional expansion on the roadmap:
- AMER: Canada, United States
- EMEA: Dublin, Frankfurt, London
- APAC: Singapore, Sydney, Tokyo
Get Started Today!
Managing data volumes is an integral part of a strong data strategy, and Splunk is here to help! To request activation in your environment, please contact your Splunk Account Team or complete this form. Include your company name, Splunk Cloud stack name, and Splunk Cloud region.
For more about Data Management and Ingest Processor, including release plans to support additional sources, destinations, and new functionality, see Splunk Docs for Ingest Processor and Splunk Docs for Splunk Cloud Platform.
Related Articles
Splunk Data Manager Enables Google Cloud Platform Data Onboarding
Introducing SPL2: The Next-Generation Search & Data Preparation Language for Splunk