Democratizing the Trusted Agentic SOC: Breaking Down Barriers to Entry
Security JK LialiasThreats move at machine speed. Defending against them should not depend on having the biggest budget, the largest team, or the ability to rebuild your security environment.
That is what democratizing the trusted agentic SOC means: making agentic capabilities easier to access, simpler to adopt, and practical for the teams organizations already have.
At Cisco Live APJC, Splunk by Cisco is announcing expanded Enterprise Security (ES) Essentials and Premier editions, Cloud Connect, and exciting enhancements to the trusted agentic SOC. Together, these updates address barriers that too often slow progress: cost, deployment complexity, and limited analyst capacity.
The Splunk platform provides the foundation, connecting machine data across security, observability, and existing tools. This shared context helps agents and analysts triage alerts, investigate threats, and coordinate response at enterprise scale.
The goal is straightforward: let agents carry more of the work while analysts remain continuously on-the-loop, controlling policy and consequential decisions. Teams can move from AI-assisted work toward increasingly autonomous operations, governed by evidence, policy, and analyst oversight.
ES Essentials More Value at the Same Price
Getting started with the agentic SOC should not require stepping up to the highest edition.
We’re expanding ES Essentials at the same price point, bringing together core agentic SOC capabilities, Agentic SOAR, Automated Threat Analysis, and base agentic capacity.
Core capabilities include autonomous triage and investigation for Tier 1 and Tier 2 work, plus specialist agents for detection and connector building. Integrated SOAR, guided response, and native phishing investigation help reduce repetitive tasks, allowing analysts to focus where judgment matters most.
This lowers the financial and operational barriers to putting agentic security to work, making a more capable SOC accessible to cost-conscious teams building their security operations.
ES Premier Scales Security Operations
As organizations adopt AI and expand agentic operations, their security needs grow too.
ES Premier includes everything in Essentials, plus advanced agentic SOC capabilities with specialist agents, native UEBA for insider threats, and four times the agentic capacity of Essentials.
Premier adds Autonomous Response, a Malware Threat Reversing agent, and Agentic Threat Hunting to support proactive defense and autonomous security operations at scale. Agents can execute permitted actions under approved policies, while analysts oversee the work and control consequential decisions.
With the two ES Editions, teams can begin with foundational agentic operations and automation, then expand toward more autonomous operations as their needs and maturity grow.
Cloud Connect Advance Without Starting Over
Cost is only one barrier. Deployment requirements should not stand between organizations and new capabilities.
Cloud Connect gives eligible self-managed ES customers access to supported cloud-delivered AI and security capabilities while retaining their existing deployment. It also helps reduce the burden of managing supporting AI infrastructure.
ES extends Cloud Connected support across familiar SOC workflows:
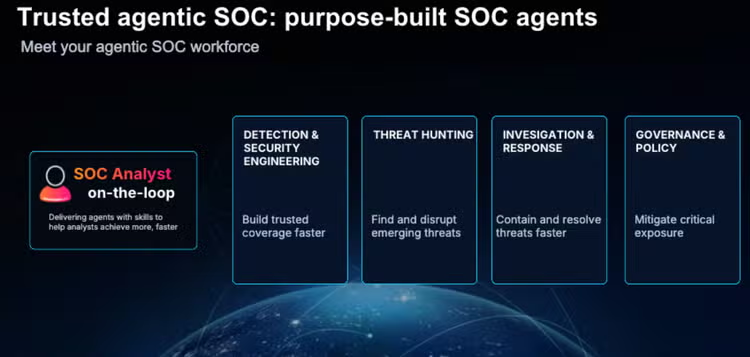
- Detection & Security Engineering: Detection Builder helps teams build and refine detections.
- Investigation & Response: Triage, guided response, and Security AI Assistant in agent mode help analysts prioritize alerts, retrieve context, and advance investigations.
Cloud Connected support for the Response Agent is also generally available for eligible self-managed ES environments. It brings investigation and response-plan context into permitted actions, with governance and analyst oversight.
Customers can build on their existing ES investment rather than make a full cloud migration their first step.
Less Manual Work, Stronger Security Coverage
Making capabilities accessible is important. Helping practitioners get value from them is what makes adoption stick.
ES strengthens agentic skills across two workforce pillars:
- Detection & Security Engineering: Detection Builder adds customizable instructions to improve consistency, accuracy, and alignment with SOC procedures. AI Threat Graph Detection, available in alpha for cloud deployments, helps surface suspicious entities from weak or hard-to-correlate signals.
- Threat Hunting: Insider Threat Agents, also in alpha, support investigations into risky user behavior and potential insider-threat signals.
These capabilities bring agentic assistance into recognizable security work, helping teams strengthen coverage without treating every agent as another disconnected tool.
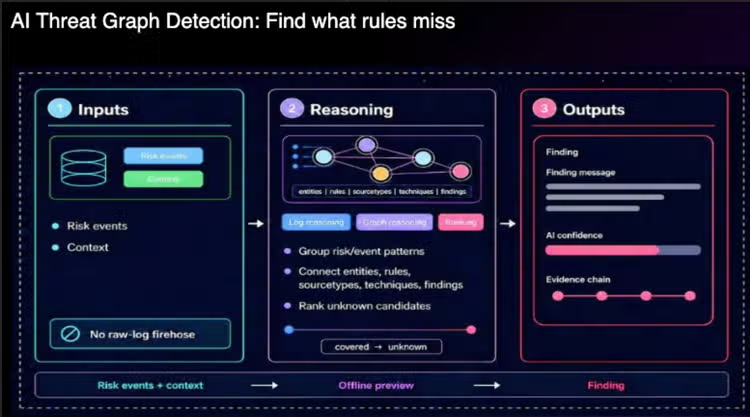
These enhancements bring agentic skills into recognizable security workflows, helping teams build coverage and investigate threats without treating every agent as another separate tool to learn.
Connect Evidence to Action
Automated Threat Analysis brings suspicious emails and artifacts into ES investigations. Investigation Aggregation groups related findings, helping analysts spend less time gathering context.
Together with guided and autonomous response, these capabilities streamline triage, investigation, and permitted actions, while analysts remain accountable for consequential decisions.
Discover and Prioritize Exposure
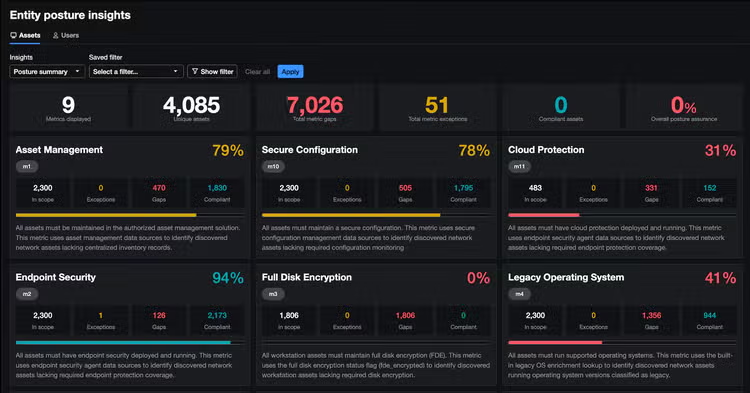
Exposure Analytics in ES connects entity exposure with context, so teams can prioritize and act on what matters. The Exposure Analytics Agent, introduced in alpha, adds AI-assisted entity investigation and exposure to emerging vulnerabilities, to help identify potential detection or remediation actions based on contextual risk.
More Ways to Start. More Room to Grow.
Expanded Essentials lowers the cost barrier. Premier extends protection and agentic capacity. Cloud Connect reduces deployment hurdles. ES brings more support into the workflows practitioners use every day.
Together, these updates move the trusted agentic SOC from a future ambition toward a more accessible operating model: grounded in data and context, built to scale analyst capacity, and governed by people.
Edition updates and individual capabilities follow their respective release schedules. Capabilities, capacity, and availability vary by edition, deployment, and release. Consult product documentation for applicable requirements.
Learn more about Splunk Enterprise Security and AI in Security to see how Splunk is helping teams build the Agentic SOC.
Related Articles
Splunk .conf26: Proving the Agentic SOC in the Center of the Community
What Generative AI Means For Cybersecurity: Risk & Reward